

George Mari @GeorgeMari@social.cleverlibre.org
- My old home page
- http://www.georgemari.com
@GeorgeMari on Twitter; Husband, Dad, Software Developer
Ask me about fixing buffer bloat, and how it has changed my life.
Joined Nov 2022
George Mari
boosted

Several postdoc and doctoral student positions also in Bayesian modeling, inference, and workflow, Gaussian processes, Bayesian neural networks, prior elicitation, probabilistic programming, etc. at Finnish Center for Artificial Intelligence, Aalto University, and University of Helsinki. I'm also one of the potential supervisors.
See more at https://fcai.fi/we-are-hiring
George Mari
boosted

George Mari
boosted

Hey everyone! I'm guessing a lot of you will be buying last minute gifts for people, and those tend to involve gift cards. Be very careful when you're buying these off-the-rack at retail stores that sell gift cards for various popular restaurants and brands. Especially those that are not in particularly tamper-proof packaging.
A friend just shared some photos he took after buying a bunch of Dardens restaurant gift cards for some gifts to clients. They didn't discover until leaving the store that several of the cards had been tampered with, their PIN scratch-offs re-covered with look-alike scratch off stickers. Also, the phony ones seem to have goofy looking barcodes, like they were scanned and printed by a laser printer without enough ink.
The trick here is the thieves pull the card out, scratch off the PIN part, record that, cover up the pin with fake tape, and then shove the thing back in the packaging and put it back on the shelf. Then, when someone buys it, the thieves can access the value on the card the minute it is activated (purchased).
The image shows two of these cards that are non-tampered (left) and two on the right that were. These cards can slide right out of their packaging with a little wiggling, and slide back in the same way.
Some stores keep their gift cards behind the counter for this reason. Might be best going for those instead of the ones in aisle 19.
George Mari
boosted

Flipboard is pivoting to ActivityPub and the fediverse https://www.theverge.com/2023/12/18/24006062/flipboard-fediverse-mastodon-activitypub-profiles-social?utm_content=buffer9ed8d&utm_medium=social&utm_source=bufferapp.com&utm_campaign=buffer

George Mari
boosted

My oldest just brought in his Arduino and breadboard and said, "Look what I made! Press the button!"
I press it and it started playing "Never Gonna Give You Up" on the piezo speaker.
George Mari
boosted

anyone looking to hire someone like me (Principal HW+GW+FW Engineer) for a job that doesn’t have periods of massive crunch? >.>
George Mari
boosted

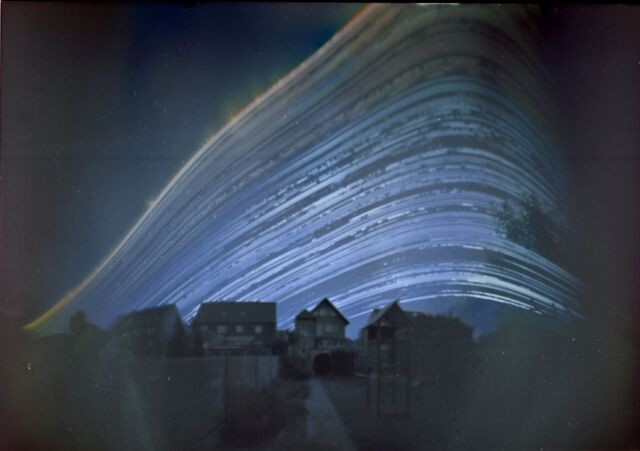
Daily Telescope: Tracking the Sun’s path every day across the sky
The image is a vivid demonstration of the changing of the seasons.
George Mari
boosted

Is there a community within Mastodon of folks who are technology minded but community / coop oriented? Like say some ‘tech for good’ kinda thing? I am really good at webdev and want to find other folks who want to help make the earth better, not burn it down with tech that only serves a small rich minority. #coop #community
George Mari
boosted

 🏳️🌈🖖🏽
2020 GOP assurances. Don’t believe them now when they claim Trump won’t be a dictator.
George Mari
boosted

George Mari
boosted

If you aren't subscribed to Democracy Docket, here is what you missed. http://democracydocket.com/me-subscribe/
George Mari
boosted

Trying to find my people on Mastodon. Please boost and follow me if you:
-Believe that mozzarella sticks are a right, not a privilege.
-Mentally greet each dog you see just in case they are telepathic.
-Think that airplanes are too heavy to fly and refuse to listen anytime someone attempts to explain the physics of it to you.
-Don't see why the government can't abolish Mondays.
-Want cats to eligible to run for president.
George Mari
boosted
This is joyous and amazing. And apparently super triggering to the right. lol. Good on you, Dr. Biden! Link in top comment.
George Mari
boosted

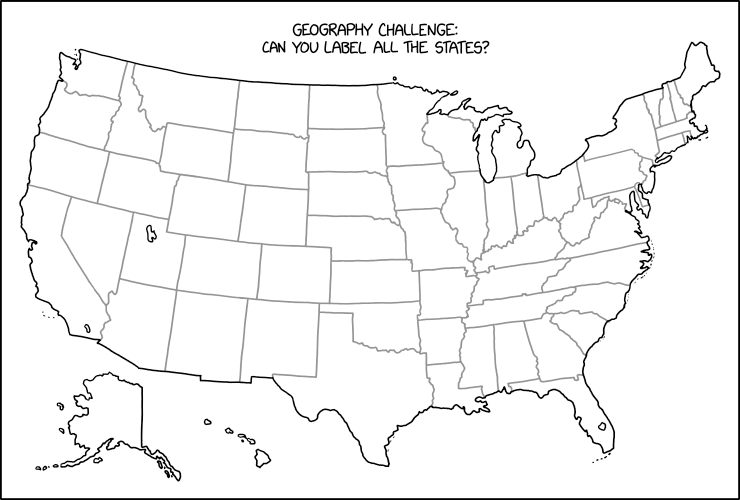
#2868 Label the States
Even with a blank map, a lot of people can only name 45-50 of the 64 states.
https://xkcd.com/2868/
George Mari
boosted

“When our students are in old and run-down buildings, it signals to them that what they do in school is of little value. It makes school less enjoyable, harder to focus.” No state spends less per student maintaining schools than Idaho. ProPublica and the Statesman show what kids and educators have to deal with.
https://www.propublica.org/article/idaho-students-educators-show-us-effects-of-underfunded-schools
George Mari
boosted

https://www.propublica.org/article/idaho-students-educators-show-us-effects-of-underfunded-schools
and
@ProPublica has an in-depth look at a horrifying situation, in Idaho where Schools have been denied funding for repairs for almost 30 years. The schools are literally falling apart. Classes are being held in stairwells and closets, amid frequent power outages, and no one is doing anything.
George Mari
boosted


"A security researcher uncovered a Twitter vulnerability in its link shortener. The vulnerability allowed an attacker to craft a malicious URL that, if a user clicked on it, would grant the attacker access to the user's account. The researcher reported the vulnerability to Twitter's bug bounty program, which closed the report as not worthy of a bug bounty. So the researcher published the vulnerability. Immediately Twitter takes its link shortener offline for hours while they fix it.But the press is only reporting on an hours-long X/Twitter link shortener outage, and has completely missed the security issues that led to it.Molly White's coverage of the vulnerability (sorry for the Xitter link but that's just the problem, literally no one else is covering this): https://twitter.com/molly0xFFF/status/1734965774517768471 "
(All quoting a friend on a private slack)
George Mari
boosted
I can't even begin to count the hours of research went into this story. Frustrated that most of that research went in the wrong direction for so long. But also very excited to share what I found, and that I finally have something to show for it all:
On Dec. 18, 2013, KrebsOnSecurity broke the news that U.S. retail giant Target was battling a wide-ranging computer intrusion that compromised more than 40 million customer payment cards over the previous month. The malware used in the Target breach included the text string “Rescator,” which also was the handle chosen by the cybercriminal who was selling all of the cards stolen from Target customers. Ten years later, KrebsOnSecurity has uncovered new clues about the real-life identity of Rescator.
https://krebsonsecurity.com/2023/12/ten-years-later-new-clues-in-the-target-breach/
George Mari
boosted





@djb @nixCraft That's a good one! I also love this one posted at https://lemmy.world/post/8434832

- My old home page
- http://www.georgemari.com
@GeorgeMari on Twitter; Husband, Dad, Software Developer
Ask me about fixing buffer bloat, and how it has changed my life.
Joined Nov 2022
