
It's fine to be able to see all pro and cons on everything, we just need to learn how to NOT get blocked by cons.
To people who cannot see them, it's easy. To us... we need more courage and constance.
But at the end of the day, we can enjoy goodness too.
Shamar
boosted
“The hacker ethos once championed as a method of subverting prevailing power has become at last its greatest lieutenant … I am not hoping for programmers to organize as a class, not anytime soon – you dudebro losers haven't got the guts – but good software simply won't be possible until we accomplish at least that much. There will never be the time or money to satisfy the guarantees our ethics require until we demand them with all the power we possess.”
https://garbados.github.io/my-blog/software_from_another_world.html
Shamar
boosted

Ridículo como animales e insectos caen en las trampas, pero no tanto cuando...
Shamar
boosted
Shamar
boosted

In the #Thunderbird #privacy notice that nobody is expected to read: https://www.mozilla.org/en-US/privacy/thunderbird/
```
Thunderbird May Disclose Information To:
Amazon Web Services: Thunderbird uses Amazon Web Services (AWS) to host its servers and as a content delivery network. Your device’s IP address is collected as part of AWS’s server logs.
```
I assume they receive and manage the crash reports on "their" servers that accidentally are owned by #Amazon.
@rysiek@mastodon.technology
Shamar
boosted


La pandemia ha fatto bene all'economia dei #GAFAM, ma qualcuno deve iniziare a occuparsi di questi ca**o di informatici!
Di @Shamar alla conferenza #AIUCD2021
http://www.tesio.it/2021/07/23/AIUCD2021_Lobbista_per_5minuti.mp4
No, indeed I surprised myself by being surprised by #Mozilla's bad faith.
I mean: ok, #Firefox is a surveillance tool marketed as a privacy friendly browser, but it's a "just" a browser.
But I was STILL thinking that good old #Thunderbird (that I do not use since decades but still suggested to others) was safe!
It's not.
#Telemetry is not just on by default and all data are received by #Mozilla through #AWS servers.
I really think such kind of defaults should be forbidden by law. And in fact they are forbidden by #GDPR as all data collection must be opt-in not opt-out.
Curiously, crash reports are disabled by default (as far as I can read online) so at least people are less likely to send them cryptographic keys in clear in a memory dump.
But the fun fact is that if you enable crash reports in the hope to let them improve a privacy friendly MUA, you sacrify your security (and your peer's security, exposing them to social engineering) to improve a surveillance software.
Indeed Thurderbird is sending back your interactions activities, so the fact that mails sent without #E2EE can be intercepted, is totally irrelevant.
@rysiek@mastodon.technology @mala
Shamar
boosted
In 2014, I gave a talk called Free is a Lie at a run-of-the-mill, dime-a-dozen, Silicon-Valley-worshiping Big Tech/surveillance capitalism conference in the Netherlands.
Yesterday, I learned that they unlisted my talk on *spit* YouTube and that it might be removed.
https://twitter.com/ribasushi/status/1418262501704282115
https://twitter.com/l18cp/status/1418281939778277380
Today, I archived it so you can keep watching it for as long as you want to.
#FreeIsALie #PeopleFarming #SiliconValley #BigTech #SurveillanceCapitalism
I wonder how I can be surprised to learn that #Mozilla's #Thunderbird collect telemetry infos (including your mail domain) and share them with partners such as #Amazon.
It's obvious they spy on your mails! 🤦♂️
Indeed, in case of crash, they even send to "their" #AWS servers a memory dump that contains sensitive data crash reports.
This likely include, your emails in clear, your private encryption keys¹ and everything else the program has loaded and kept in memory.
What does this means for an hypothetical attacker that can access such reports?
I mean... like a #USA agency arguing that you might be a terrorist or something.
Oh but sure... they shall do no evil...
https://www.mozilla.org/en-US/privacy/thunderbird/
#Privacy #Freedom #hypocrisy #Security #infosec
_____
1) Since version 68, Thunderbird does not use the #GPG suite via #Enigmail, but directly do encryption "to avoid licensing issues" 🤷♂️
@rysiek@mastodon.technology @mala
@rysiek@mastodon.technology
Does derivative tools like #Seamonkey or #LibreWolf count as #Mozilla tools?
What about #Rust?
Shamar
boosted
Libreboot pre-installed laptops are back in stock on https://retrofreedom.com/
Shamar
boosted


RT @emmevilla
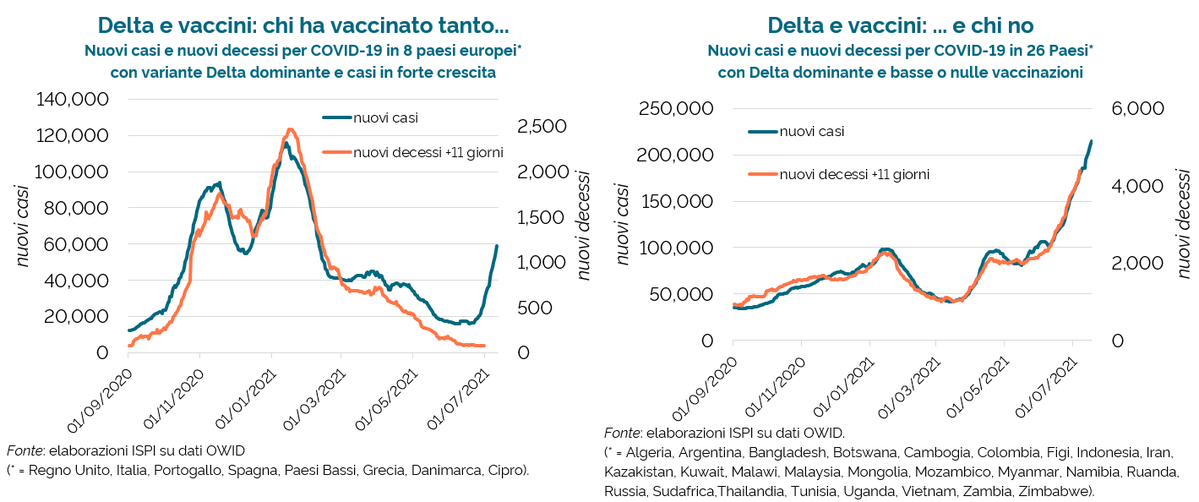
🦠🌍 Volete la prova definitiva che i #vaccini ci stanno salvando?
Eccola.
A sinistra, 8 paesi che hanno vaccinato molto.
A destra, 26 paesi che hanno vaccinato pochissimo.
Trovate le differenze.
E #vaccinatevi.
Shamar
boosted
@rysiek@mastodon.technology
It's not that simple.
In the article you liked #OCCRP explains
```
This is normally done through the target’s mobile operator, which some governments can access or control.
```
How many CA are state-run agency? How many CDNs (behind HTTPS) can be subject to similar impositions?
If a state can impose to a mobile operator to track a citizen, why do you think it cannot impose to serve certain DNS records, certain TLS certificate and so on to certain people only?
Also, HTTPS leaks a lot of information about every visitor to the site owner (IP, cookies) and you are assuming the hosting/cloud provider is not malicious, while often it is.
And these leaks apply to everybody, not just to targetted victims.
You just need to control/compromise a single hosting/cloud provider and attract the victim on one of its HTTPS websites to install the same malware without the website owner knowing anything AND without the victim suspecting anything (it's HTTPS, so it's safe, isn't it?)
On the other hand, HTTP proxies can cache requests and hide you from the server.
It's dumb to blame http website owner for the victims killed by criminals and governments: it's the whole Web that is broken and insecure at heart, HTTPS or not.
We need people to understand how it works in depth so that they can foresee the risks.
A false sense of security is MORE dangerous than a known state of insecurity.
Shamar
boosted


It was hard for me to tell how serious the Audacity stuff was
but the original version of this comment (see edit history) is a threat of deportation and insinuation that if they don't comply with a takedown you hope they'll be imprisoned, killed, or tortured by their country of origin https://github.com/Xmader/musescore-downloader/issues/5#issuecomment-882450335
and so yeah okay thanks for making that clear
(also thx for the link @Claire)
- O.S.
- http://jehanne.io
Joined May 2019
