

Nick @internic@social.cleverlibre.org
- Pronouns
- he/him/his
Theoretical physicist by training (PhD in quantum open systems/quantum information), University lecturer for a bit, and currently paying the bills as an engineer working in optical communication (implementation) and quantum communication (concepts), though still pursuing a little science on the side. I'm interested in physics and math, of course, but I enjoy learning about really any area of science, philosophy, and many other academic areas as well. My biggest other interest is hiking and generally being out in nature.
Joined Nov 2022
Nick
boosted

THUNDERBIRD 115 SUPERNOVA IS HERE! 🎉🍾
With this year’s version, we’re delivering much more than just another yearly release. Supernova represents a modernized overhaul of the software – both visually and technically – while retaining the familiarity and flexibility you expect.
It's your first step into the future of Thunderbird.
Get the details here:
https://blog.thunderbird.net/2023/07/our-fastest-most-beautiful-release-ever-thunderbird-115-supernova-is-here/
Nick
boosted

Exhibit 1, Greg Corrado of Google on Med-PaLM 2, their AI chatbot
Exhibit 2: an unnamed Boeing engineer on the 737 Max
Nick
boosted
A good, close look at current global temperature spikes, and inherent climate variability https://theconversation.com/global-temperature-rises-in-steps-heres-why-we-can-expect-a-steep-climb-this-year-and-next-209385
#climate #ClimateShock
Nick
boosted

I challenge Shakaar to a nose ridge measuring contest!
Nick
boosted

Hackers are using open source software that’s popular with video game cheaters to allow their Windows-based malware to bypass restrictions Microsoft put in place to prevent such infections from occurring.
The software comes in the form of two software tools that are available on GitHub. Cheaters use them to digitally sign malicious system drivers so they can modify video games in ways that give the player an unfair advantage. The drivers clear the considerable hurdle required for the cheat code to run inside the Windows kernel, the fortified layer of the operating system reserved for the most critical and sensitive functions.
Researchers from Cisco’s Talos security team said Tuesday that multiple Chinese-speaking threat groups have repurposed the tools—one called HookSignTool and the other FuckCertVerifyTimeValidity. Instead of using the kernel access for cheating, the threat actors use it to give their malware capabilities it wouldn’t otherwise have.
Malware developers with admin privileges already had one well-known way to easily bypass the driver restrictions. The technique is known as “bring your own vulnerable driver.” It works by loading a publicly available third-party driver that has already been signed and later is found to contain a vulnerability allowing system takeover. The hackers install the driver post exploit and then exploit the driver vulnerability to inject their malware into the Windows kernel.
Although the technique has existed for more than a decade, Microsoft has yet to devise working defenses and has yet to provide any actionable guidance on mitigating the threat despite one of its executives publicly lauding the efficacy of Windows to defend against it.
The technique Talos has discovered represents a new way to bypass Windows driver restrictions. It exploits a loophole that has existed since the start of the policy that grandfathers in older drivers even when they haven’t been reviewed for safety by Microsoft. The exception, designed to ensure older software was still able to run on Windows systems, is triggered when a driver is signed by a Windows-trusted certificate authority prior to July 29, 2015.
“If a driver is successfully signed this way, it will not be prevented from being installed and started as a service,” Tuesday’s Talos post explained. “As a result, multiple open source tools have been developed to exploit this loophole. This is a known technique though often overlooked despite posing a serious threat to Windows systems and being relatively easy to perform due in part to the tooling being publicly available.”
From: Hackers exploit gaping Windows loophole to give their malware kernel access
Nick
boosted

“Zuck is boring dystopian. Zuck is detached corporatism pervading our daily lives. He's loathsome, and while not entirely predictable, forecastable.
Musk is Veruca Salt if she grew up on
4chan.”
https://reddit.com/r/news/comments/14ul3iw/suspended_twitter_account_tracking_elon_musks_jet/
Nick
boosted

Just in time for the 2024 U.S. elections season!
https://www.truthorfiction.com/meta-facebook-2024-election-disinformation-team-cuts/
Nick
boosted

In a strange and dramatic sentencing hearing today, the Silk Road saga ended with the legendary dark web market's second-in-command Variety Jones being sentenced to two decades behind bars. https://www.wired.com/story/silk-road-variety-jones-sentencing/
Nick
boosted

@hacks4pancakes Any ethernet port in a storm
Nick
boosted


This is some incredibly janky shit. I’m exhausted and kind of proud
@Pippilngstkg@mstdn.social Sounds like this probably won't be the big deal that was originally reported.
https://vmst.io/@WestportObservatory/110695935999258506
#northernLights #aurora #auroraBorealis #spaceWeather
Nick
boosted

Heard about a big #NorthernLights display this week? Don't believe the hype. Reports over the weekend claimed a major solar storm was forecast for later this week and could produce auroras at mid-latitudes. Space scientists, though, backed away from those predictions on Monday, saying the #aurora will likely be limited to Alaska and Canada and not make it further south.
https://www.nbcnews.com/science/science-news/northern-lights-visible-17-states-rcna93390
Nick
boosted

Nick
boosted

Hackers exploit gaping Windows loophole to give their malware kernel access
Microsoft blocks a new batch of system drivers, but the loophole empowering them remains.
Nick
boosted

Once the hype will die down (it is never going to be too early), it is clear to me that the machine learning applications that will stand the test of time are the one that automate a task that is long and boring to do, but it is easy to check whether it has been done properly.
Nick
boosted

Hey geeks! Bea Wolf is, for two days, just 10 bucks on Amazon! That for just 10,000$ you can get a thousand copies!
https://www.amazon.com/Bea-Wolf-Zach-Weinersmith/dp/1250776295
Nick
boosted

Ron DeSantis from FLORIDA flew 36 migrants from TEXAS and dumped them in #Sacramento — and my colleague’s (Rabbi Mona Alfi’s) synagogue served them dinner, gave them basic supplies and temporary housing. And this inhumane guy is running for President? I shudder to think. #migration #desantis
Nick
boosted
Today was, btw, the first time someone said hello to me at a conference because they met me on mastodon  💜
(Also met multiple ppl I knew or who knew me from twitter - the professional #astrodon community is still stronger there, but hey, we are building something new here...)
Nick
boosted

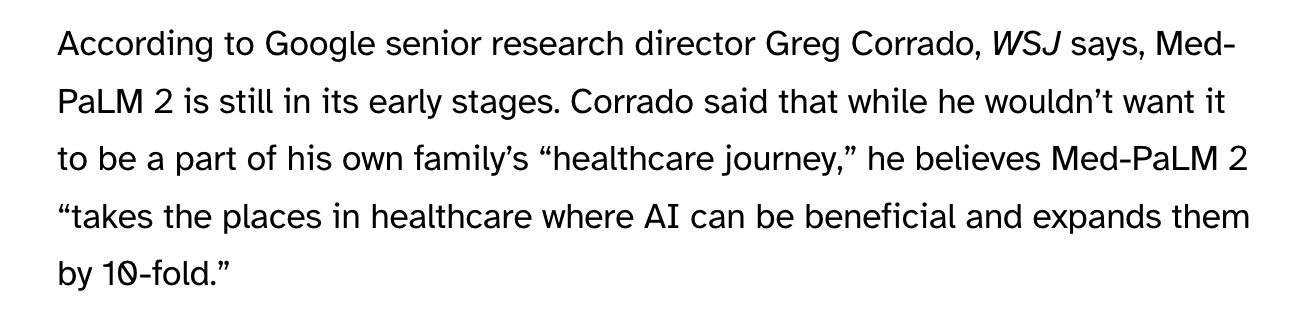
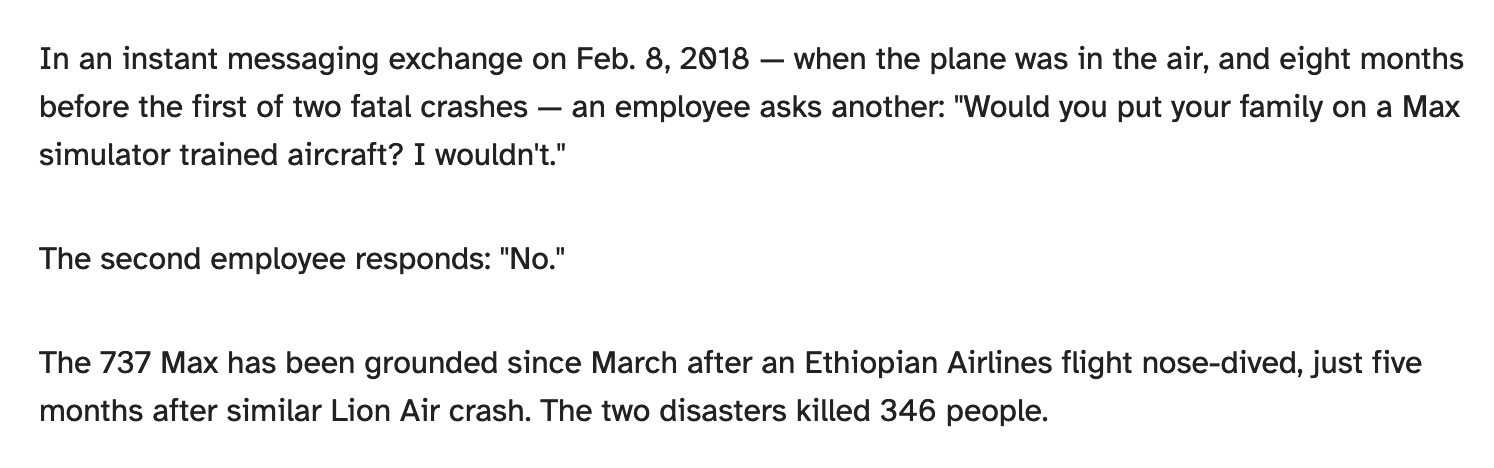



Cherry on top: Arkham's referral links for this service are just Base64-encoded email addresses, meaning anonymous crypto people who are sharing the referral links have inadvertently revealed email addresses they didn't realize would be linked to them.
Nick
boosted
You may have heard that climate change is contributing to a global #sriracha shortage and we're here to tell you that's completely true:
https://www.truthorfiction.com/why-sriracha-is-out-of-stock-everywhere/
- Pronouns
- he/him/his
Theoretical physicist by training (PhD in quantum open systems/quantum information), University lecturer for a bit, and currently paying the bills as an engineer working in optical communication (implementation) and quantum communication (concepts), though still pursuing a little science on the side. I'm interested in physics and math, of course, but I enjoy learning about really any area of science, philosophy, and many other academic areas as well. My biggest other interest is hiking and generally being out in nature.
Joined Nov 2022
