

Nick @internic@social.cleverlibre.org
- Pronouns
- he/him/his
Theoretical physicist by training (PhD in quantum open systems/quantum information), University lecturer for a bit, and currently paying the bills as an engineer working in optical communication (implementation) and quantum communication (concepts), though still pursuing a little science on the side. I'm interested in physics and math, of course, but I enjoy learning about really any area of science, philosophy, and many other academic areas as well. My biggest other interest is hiking and generally being out in nature.
Joined Nov 2022
Nick
boosted

Eric Adams is using AI to make New Yorkers think he speaks their language, which experts called "Orwellian."
https://www.vice.com/en/article/xgw78a/nyc-mayor-casually-announces-hes-deepfaking-himself-experts-horrified?at_medium=Social%20media&at_campaign=Mastodon
#Technews #ericadams #NYC #AI #deepfake
Nick
boosted

“I just always assumed, despite the fact that the US hadn’t sent any women up there, or people of color, that I was going to go.”
Dr. Mae Jemison (@maejemison) was born #OTD in 1956. Doctor, peace corps volunteer, first Black woman in space, and first astronaut on Star Trek.
Nick
boosted

Enjoying “An Immense World” by Ed Yong, on animal senses. I think I heard once before that scallops have up to 200 eyes with mirrors made from guanine crystals, but failed to be sufficiently amazed at the time, so I’m glad to have been reminded.
Nick
boosted

Under FIDO, to which Google declares compliance for passkeys[^1], the private key should never leave the client device so they shouldn’t be stored on the server… but that applies to the service provider (e.g. Shopify website). Identity provider, in this case Google or Apple, of course do store private keys on their servers for backup purposes, only they declare them to be encrypted by the sync passphrase.
I guess there are two workflows here: one under normal usage scenarios, one under TAO[^2] or other “law enforcement love letter” scenarios.
Granted that identity like Google provider controls all data flows for any software keys, from storage (Android), sync passphrase entry (Android) to operating system and application updates (especially after hosted developer keys were introduced to Android[^3]), it would be naive to have any illusions that under TAO scenario they won’t retrieve that one way or another.
This shouldn’t be the case with hardware authenticators, of course, which are also allowed by Passkeys. Or at least building a side channel for private key retrieval will be much more difficult even in TAO scenario.
[^1]: https://developers.google.com/identity/passkeys
[^2]: https://en.wikipedia.org/wiki/Tailored_Access_Operations
[^3]: https://www.theregister.com/2021/07/01/android_app_bundle/
Nick
boosted

Pretty much exactly 19 years ago I got on a train to Oxford and made Mark Shuttleworth's laptop successfully suspend and resume using ACPI and that was the turning point in my entire career
Nick
boosted

Very insightful analysis in this piece from Cory Doctorow (@pluralistic) -- a succinct and accessible summary of the intersection between IT and Politics in 2023.
If you know someone struggling to understand why they should care about digital privacy and data rights, just send them this.
https://theintercept.com/2023/10/16/surveillance-state-big-tech/
Nick
boosted

Do you want to know why companies keep trying to get you to install their app? @pluralistic has the answer:
"An app is best understood as “a webpage wrapped in just enough IP to make it a crime to install an ad blocker” (or anything else the app’s shareholders disapprove of)."
https://theintercept.com/2023/10/16/surveillance-state-big-tech/
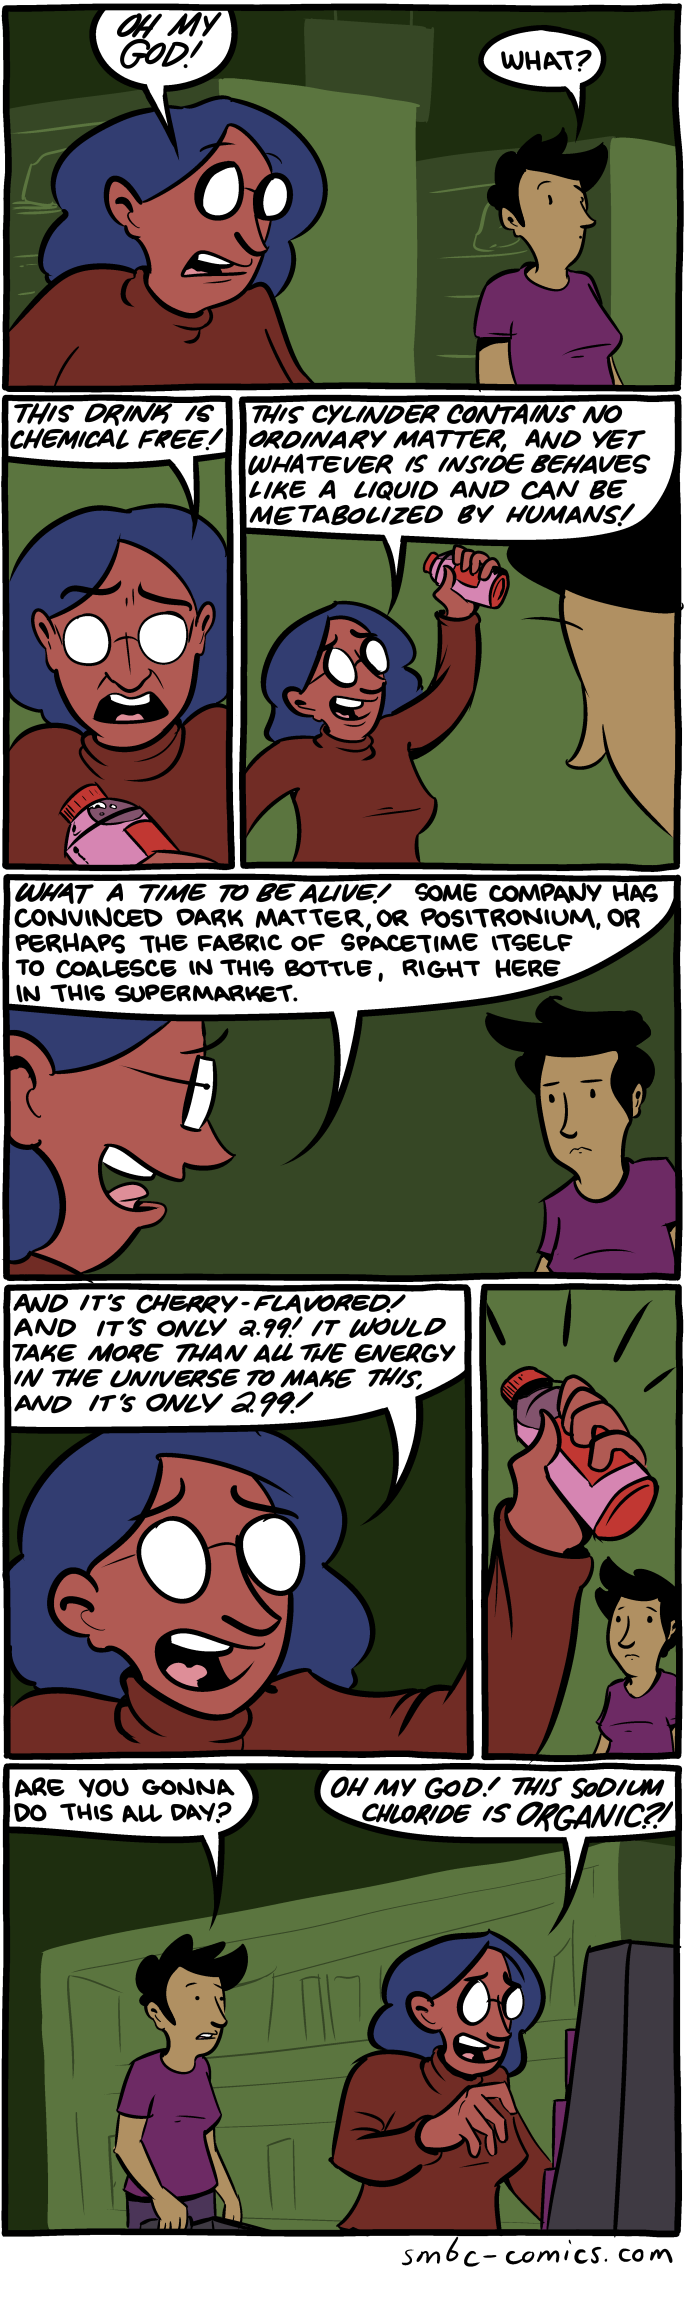
@CStamp I think of this comic every time someone says something has "no chemicals."
https://www.smbc-comics.com/?id=3324
Nick
boosted

Everyone knows that all food is made of chemicals, right?
Do you know what contains glycosylated flavonoids, phenolic acids, carotenoids, the vitamin B groups, ascorbic acid, tocopherols, and sesquiterpene lactones?
Lettuce.
Nick
boosted

There are *ads* in the *start bar* in Windows 11, in an operating system I paid for. Whose joke of enshittification is this?
Nick
boosted

The Promenade in Star Trek Deep Space 9 has some businesses you wouldn't expect.
When in production in the 90s I'm guessing staff never assumed this would become public. (A Thread)
#StarTrek #DS9 #DeepSpace9 #ContentWarningUnbridledNerdiness
Nick
boosted

In case folks aren't aware, the Internet Archive now has a scholar version with a huge collection of academic work available.
#academicchatter #academicmastodon #academic #education #open
Nick
boosted

People are annoyed by Youtube ads. Instead of spending too much energy to disable ads, start to upload your videos on Peertube:
Peertube is to Youtube what Mastodon is to Twitter. But better because people don’t need to create an account, they can subscribe to your videos channel directely with their Mastodon account (or other Fediverse tool).
My video channel: @oneploumshow
Let’s raise awareness about Peertube:
Nick
boosted

One of the world's largest online travel agencies, Booking.com, is being used by fraudsters to trick hotel guests into handing over their payment card details.
How do I know? The fraudsters tried the trick with me.
@MichaelPorter Somewhat in this vein, I had lunch with a friends (both physicists) recently, and they were talking about their kids' homework (4th grade, I think) and how one of their math problems was ill-defined. They said that the most reasonable literal interpretation would require a complex combinatorial calculation.
I said that the students of physicists (and presumably other STEM types) require special teachers, not so much to deal with the students as to deal with the parents. ;-)
@MichaelPorter I'm not a math teacher per se, but I have certainly taught plenty of people plenty of math, so hopefully that's close enough.
I think the short answer is that there is not complete agreement. It's often surprising to people how non-uniform people (even mathematicians) are about their use of mathematical notation. I think I dimly recall that I was originally taught like A, but as my education progressed certainly B became predominant.
One way of viewing it is whether you are treating the square root as a function or a relation. If it's a relation on real numbers then it can have multiple values satisfying the relation as in A. In the relation viewpoint, line 2A would be basically a tautology. If it's a function then in the standard understanding of the term it would necessarily only have a single value (though in some contexts sometimes people do use terms like "multi-valued function"), so you need to specify plus or minus to encompass all solutions, as in 2B. As others have mentioned, in complex analysis you can take another way out of this conundrum using Riemann surfaces, but that doesn't seem useful for your current situation.
In my experience the viewpoint of treating the square root as a function is more predominant, perhaps in part because it then leads more neatly into discussions of functions in calculus. If I were grading papers, I probably wouldn't mark either as wrong, but I would probably teach it according to B.
As to which to teach your niece, I guess it probably depends on whether you're trying to 1) use the most pedagogically effective, 2) use what she's most likely to see again later, or 3) use what the teacher considers "correct". I don't know the empirical answer to (1). I suspect B is the answer to (2). And none of us can know the answer to (3) for sure; based on my own experience B seems more likely, but it's not a sure thing.
Nick
boosted

Threat intel people: if you are at a company that can offer 404 Media tools, data, resources, and you want help our journalism, get in touch. I'm continuing to cover criminal groups, drug traffickers etc. I have pDNS, always interested in other tools
Obviously we went from salaries to $0. As a four person startup we don't have the funds to pay for access to certain tools. Some people already like what we do in general and help out. Email, DM or Signal if there is anything you think would be useful to us.
https://www.404media.co/high-life-hackers-national-menace-acg-the-comm-braiden-williams/
Nick
boosted

I just learned about subplot mosaics in @matplotlib today, and I think it's neat.
https://matplotlib.org/stable/api/_as_gen/matplotlib.pyplot.subplot_mosaic.html
Nick
boosted

Mathematicians and math educators only, please. Which is correct?
(Background - Math was my best subject, but it was decades ago, and now that I’m tutoring my niece I run into things like this… This is a genuine request for assistance, not a trap!)
At some point, probably long after I left a math class, I started assuming the square root sign meant both roots. I am now becoming aware that it only means the principal (positive) root, and if you want both roots you have to be explicit.
Comments very welcome.
Nick
boosted




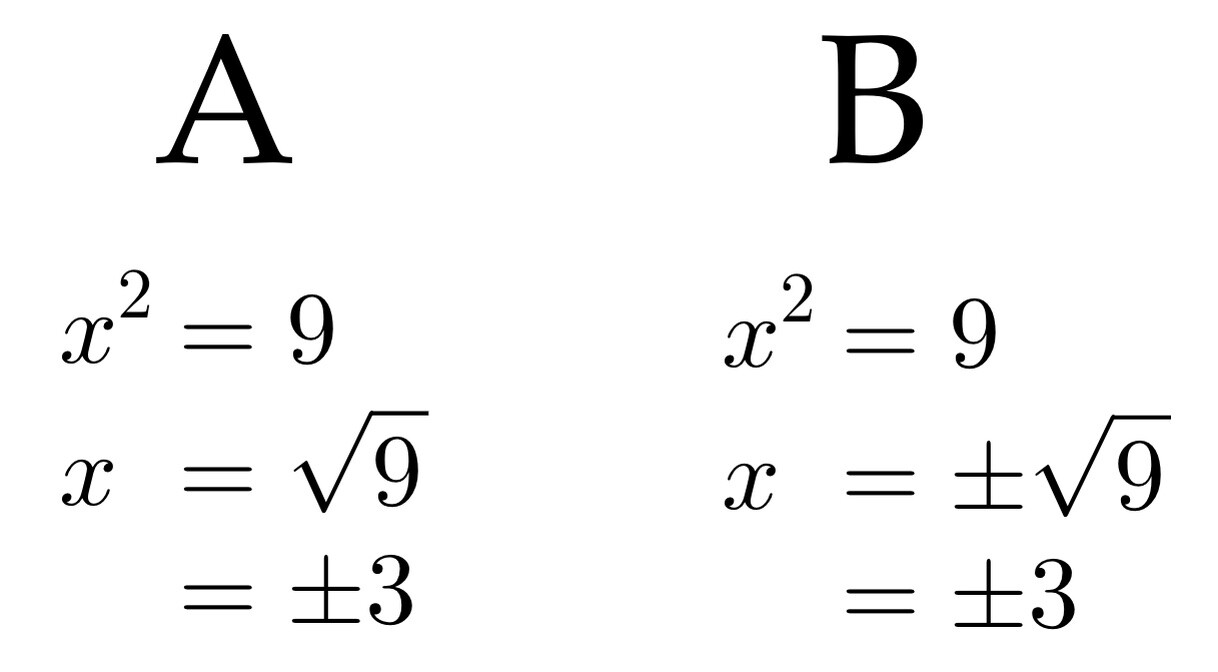
The HTTP/2 protocol 0-day got a lot of attention last week. It was definitely a big deal, as evidenced by its ability to cause 4xx and 5xx errors for Cloudflare customers. But the thing I think a lot of people didn't understand is the vulnerability really only affected load balancers and super big cloud providers. They were all patched by the time we learned of the vulnerability. What I think a lot of people lost sight of was that there are already a million other easier ways to DDoS smaller players who had yet to patch, so they weren't really affected.
- Pronouns
- he/him/his
Theoretical physicist by training (PhD in quantum open systems/quantum information), University lecturer for a bit, and currently paying the bills as an engineer working in optical communication (implementation) and quantum communication (concepts), though still pursuing a little science on the side. I'm interested in physics and math, of course, but I enjoy learning about really any area of science, philosophy, and many other academic areas as well. My biggest other interest is hiking and generally being out in nature.
Joined Nov 2022
