

Lup Yuen Lee 李立源 @lupyuen@social.cleverlibre.org
- Pronouns/Gender/Sexuality
- He/Him/They, Bisexual/Asexual 🇸🇬
- Date of Birth
- 1969
- Articles
- https://lupyuen.codeberg.page
IoT Techie and Educator / Apache NuttX PMC
Joined Jan 2020
Creating a Pick and Place control board with the RP2040
https://blog.thea.codes/starfish-a-control-board-with-the-rp2040/
Lup Yuen Lee 李立源
boosted

Found it on this page
https://joinmastodon.org/servers
Lup Yuen Lee 李立源
boosted

@cstanhope @lupyuen Yeah, it's unfortunate. Many Flatpak advocates including myself characterize this issue as being part of a 'transition' in the Linux desktop: Many apps weren't built for the Flatpak sandbox, so they heavily demand permissions. With time, more will hopefully adjust their standards to comply.
I'll add an edit to the article that explicitly points out that while Flatpak has sandboxing capabilities and Flathub encourages people to use them, Flatpak itself doesn't mandate them.
"With Twitter in chaos, Mastodon is on fire"
Tao Huabi: the driving force behind crunchy chilli sensation Lao Gan Ma
Lup Yuen Lee 李立源
boosted

@lupyuen I have a bias as I have long benefited from the traditional Linux distro model, and I have never encountered "depdency hell" on Linux *except* when I attempt to install 3rd party software (whether built from source or as a binary) outside the distro's channels, which is not unexpected.
But I will not pretend there are not issues, or rather, tradeoffs made in that model. Flathub may help, but all those new packages feel a bit like:
Lup Yuen Lee 李立源
boosted
@lupyuen Also, when extolling the virtues of sandboxed containers and explicit permissions of flatpaks, this seems like a *really* big caveat to not gloss over:
"It’s important to mention that many apps on the biggest Flatpak app store, Flathub, aren’t sandboxed particularly well."
Lup Yuen Lee 李立源
boosted

 🇳🇱
> First, it will never be the year of the "Linux desktop", as Linux is only a kernel and doesn't operate on its own.
Did you mean systemd/Linux?
Cant say this makes sense. Obviously linux needs many things to run and doesnt run on its own. It needs systemd, gnu userland, a x86 cpu, a motherboard, electricity, etc.. we dont say "Today is the year of linux, systemd, x86, motherboard, electricity"... we just say linux.
why, because its the component we care about in this discussion. We are sayi g "is this the year desktops finally start using linux as its kernel".
@tekkie Thanks, great to see you here! :-)
Lup Yuen Lee 李立源
boosted
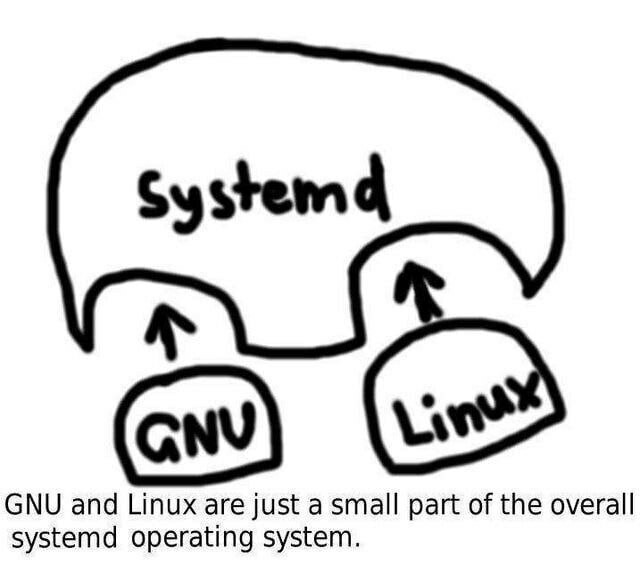
@lupyuen First, it will never be the year of the "Linux desktop", as Linux is only a kernel and doesn't operate on its own.
Did you mean systemd/Linux?
I tried to read that article, but the example it gave was installing the proprietary malware known as steam, so I stopped reading.
The fact is, the kernel, Linux's SYSCALL ABI for each architecture does not change once it is stabilized.
You can run a statically linked elf from 1998 that only uses Linux SYSCALLs and it'll work today.
But, generally binaries are dynamically linked for security and sanity reasons and so you can't just copy those between systems and expect them to work.
Even so, generally libraries like glibc are forwards compatible, but you can't expect the ABI to be the same after 20 years - only the API.
As a result, the real packaging solution is to compile from source and let the compiler and build scripts to the rest.
Gentoo-libre and Guix is an example of how to properly manage packaging.
Really, you only have issues with packaging when it comes to using proprietary malware, as you can't compile software you only have the binaries of, as a result, the real solution is to just not use proprietary malware.
Fancy modules for #PinePhone's Allwinner A64 Display Engine
Source: https://lupyuen.github.io/articles/de?1#appendix-initialising-the-allwinner-a64-display-engine
"Distribution packaging for #Linux desktop applications is unsustainable"
Lup Yuen Lee 李立源
boosted

I can’t wait to read them. I have a few of those lanterns in safe places, with rolls of wicks and a little fuel stored up too. I’ll be happy to see what other insights your articles and or posts, will illuminate.
Homebrew "rvPhone" aims to be the first #RISCV mobile experiment
https://tuxphones.com/risc-v-phone-rvphone-imx8-esp32-sim7600x-e310-nlnet-majstor/
Z-Library eBook site domains seized by U.S. Dept of Justice
Lup Yuen Lee 李立源
boosted


@lupyuen kinda reminded of the time microsoft tried to put that 'strong naming' thing in to .NET, which was something like including the signature of a library when you marked it as a dependency.
- Pronouns/Gender/Sexuality
- He/Him/They, Bisexual/Asexual 🇸🇬
- Date of Birth
- 1969
- Articles
- https://lupyuen.codeberg.page
IoT Techie and Educator / Apache NuttX PMC
Joined Jan 2020
