

Lup Yuen Lee 李立源 @lupyuen@social.cleverlibre.org
- Pronouns/Gender/Sexuality
- He/Him/They, Bisexual/Asexual 🇸🇬
- Date of Birth
- 1969
- Articles
- https://lupyuen.codeberg.page
IoT Techie and Educator / Apache NuttX PMC
Joined Jan 2020
Beginner's Guide to HackRF (Software-Defined Radio)
#RISCV Address Translation for Sv39 Memory Mgmt Unit
Article: https://lupyuen.codeberg.page/articles/mmu.html#appendix-address-translation
Lup Yuen Lee 李立源
boosted

Lup Yuen Lee 李立源
boosted

@tasket @caligari @lupyuen It's not difficult to follow a signal. Ransomware attacks aren't going to be far behind as some of those systems use multiple wireless sensors.
They are difficult to open without using a Dremel. I've cut myself a few times with Xacto blades trying to get through that thick sonic welded plastic shell. At least the app wasn't too difficult to peek at. White listing devices and some other things that might possibly be going on.
There has to be a way to get in without bleeding everywhere. 
Blinking an LED in #NimLang ... With Apache #NuttX RTOS
Source: https://github.com/lupyuen/nuttx-nim#blink-an-led-with-nim
Indra Nooyi: "My Life in Full" (PepsiCo Ex-CEO)
How Apache #NuttX RTOS swaps the #RISCV Page Tables for Kernel and Apps
Article: https://lupyuen.codeberg.page/articles/mmu.html#swap-the-satp-register
Lup Yuen Lee 李立源
boosted

@tasket @lupyuen 1. To avoid extra controllers (cost, mobility); 2. To integrate with other services like online monitoring (not specifically cloud but dependant people); 3. To facilitate free market (user's freedom) . The other side is the why not? BLE is widely supported and in continuous improvement. Does a non standard or privative technology guarantee full security (protected against malicious people, in this case) on well-being devices?
"2023 showcased the power and perils of #OpenSource"
https://techcrunch.com/2023/12/26/the-eternal-struggle-between-open-source-and-proprietary-software/
Lup Yuen Lee 李立源
boosted

@lupyuen Maybe not true now, but one thing I discovered about the dbus-daemon, when I studied it years ago for a company project, was that it could block the root user from using D-Bus. That might have unexpected side-effects.
"Software Developers must continually Learn in order to keep up with the fast-paced changes in the field"
Emulating an iPod Touch 2G using #QEMU (ARMv6)
"Croquet was originally implemented in Squeak ... derived from Apple Smalltalk-80"
Lup Yuen Lee 李立源
boosted


@lupyuen I'd have to question why anyone's insulin pump is controlled by an android device OR bluetooth.
Mapping the Virtual Memory for #NuttX Apps ... With #RISCV Sv39 Page Tables
Article: https://lupyuen.codeberg.page/articles/mmu.html#user-levels-1-and-2

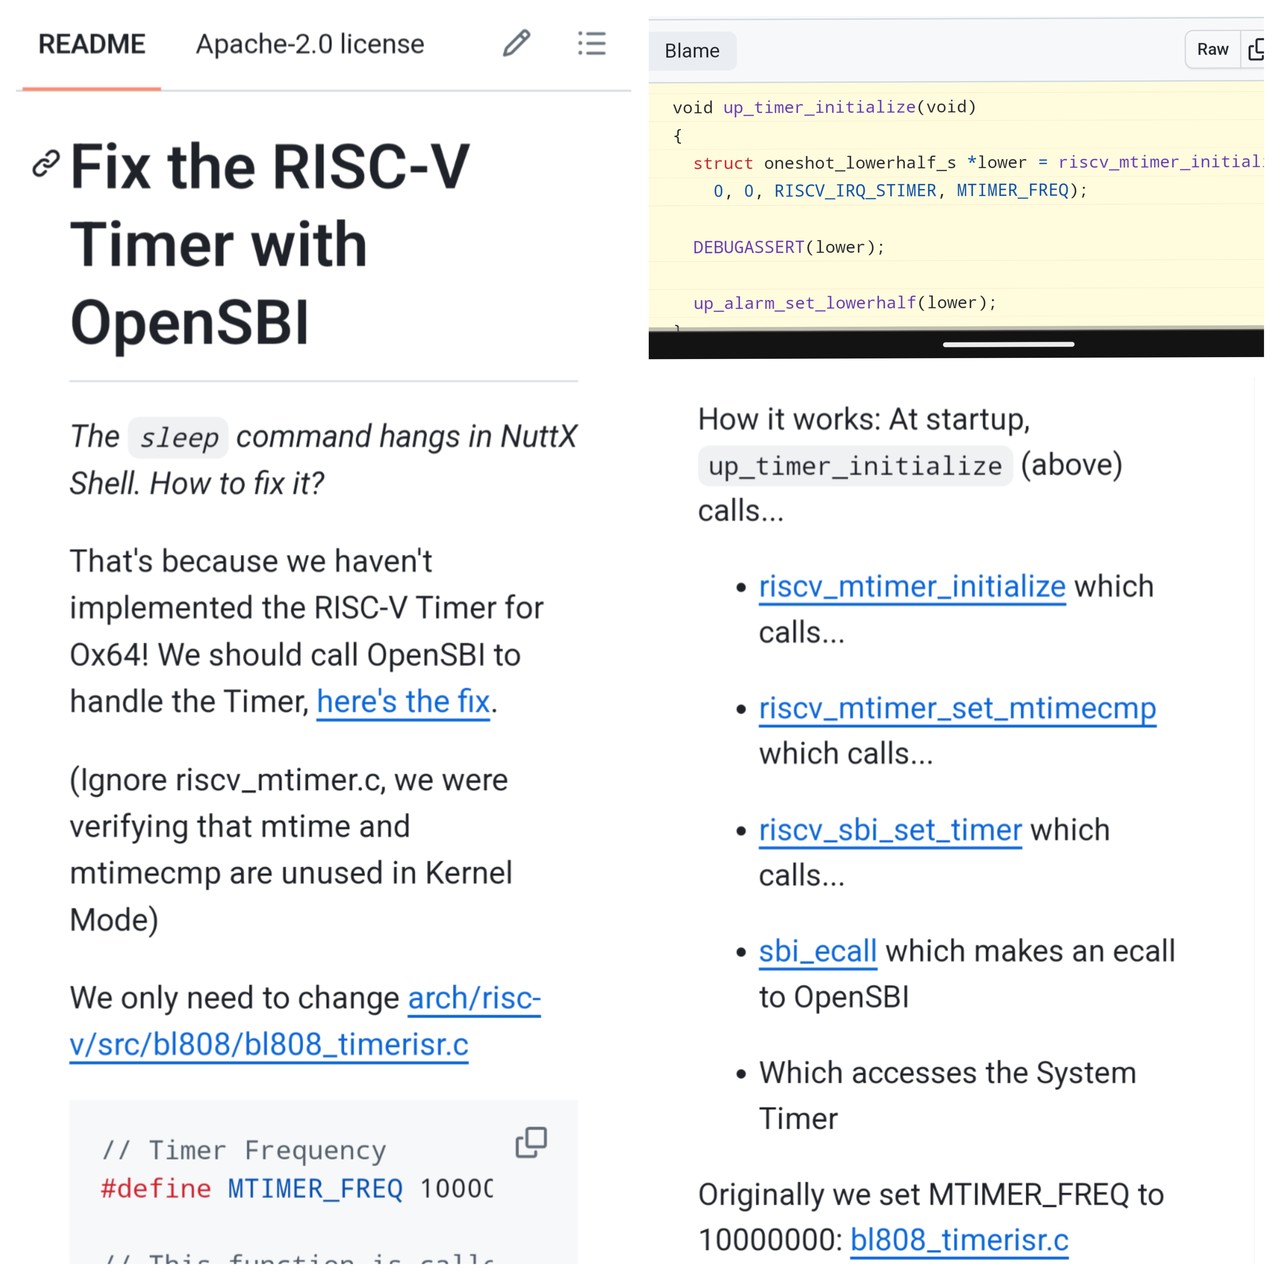
Fixing the #RISCV Timer in Apache #NuttX RTOS with OpenSBI
Source: https://github.com/lupyuen/nuttx-ox64#fix-the-risc-v-timer-with-opensbi
- Pronouns/Gender/Sexuality
- He/Him/They, Bisexual/Asexual 🇸🇬
- Date of Birth
- 1969
- Articles
- https://lupyuen.codeberg.page
IoT Techie and Educator / Apache NuttX PMC
Joined Jan 2020
