

modrobert @modrobert@social.cleverlibre.org
- PGP
- 0x09208346d9245e65
- GitHub
- https://github.com/modrobert
- https://twitter.com/modrobert
- Bitcoin
- bc1qtxmtnc225p767x78k0xwcnhr0u64r655kqvc69
-"When the going gets weird, the weird turn pro..."
Joined Sep 2018
@pancake Thanks! Yes, the mastodon bridge sounds interesting.
"Risky Biz News: Chinese APT hacks subsidiaries, pivots to corporate headquarters
In other news: Google and Mozilla patch another Chrome & Firefox zero-day; Cisco patches its own zero-day; and new DarkRiver APT targets Russian defense sector."
https://riskybiznews.substack.com/p/chinese-apt-hacks-subsidiaries
@pancake OK, thanks for checking.
@malwaretech I'm guessing some mainstream news website, whatever it is, doubting very much it's something like: thegrayzone.com
@radareorg @pancake I tried using llama-2-7b-chat-codeCherryPop.Q5_K_M.gguf instead of llama-2-7b-chat-codeCherryPop.ggmlv3.q4_K_M.gguf, it's roughly 700mb bigger, gives similar results but supposedly more accurate ("large, very low quality loss - recommended"). Got it from here:
https://huggingface.co/TheBloke/llama2-7b-chat-codeCherryPop-qLoRA-GGUF
modrobert
boosted


The slides for the #radare2 #ai presentation made by @pancake are now public! Check them out while they are still hot! https://github.com/radareorg/radare2-extras/blob/master/r2ai/local/r2ai.pdf
@pancake Does that still require you to have AI API access, or does it work stand-alone? I'm still learning how it works in detail.
"Risky Biz News: China admits NSA hacked Huawei
In other news: iOS zero-days used to hack Egyptian presidential candidate; new Sandman APT targets telcos across the world; Russia's largest travel agency breached by pro-Ukraine hackers."
https://riskybiznews.substack.com/p/china-says-nsa-hacked-huawei
@freemo I don't know what payment methods X accepts, was assuming it will require some kind of billing address (thinking KYC).
@freemo While paying might solve the bot problem, it also means you have to identify yourself which is bad if you care about privacy.
@malwaretech Improvise and adapt.
modrobert
boosted

How about a Friday WIP video? Metal Gear for the MD/Genesis. #metalgear #genesis #megadrive
modrobert
boosted

#libwebp 1.3.2 has two #security related flaws that have been fixed in main:
• Fix invalid incremental decoding check:
https://github.com/webmproject/libwebp/commit/95ea5226c870449522240ccff26f0b006037c520
• Fix next is invalid pointer when WebPSafeMalloc fails:
https://github.com/webmproject/libwebp/commit/dce8397fec159c9edfeec7c6388cb81428c87ed8
While these are not as easy to exploit as CVE-2023-4863 it seems evident that there has been some gaps in libwebp fuzzing at google. Also CVE-2023-4863 was obviously assigned to a wrong project. #infosec #vulnerabilities #cve
modrobert
boosted

brutal first blood for cytrox on iOS 17, but also damn that's some clear cut misuse.
modrobert
boosted
if this infosec stuff doesn't work i'll start an ice cream shop
modrobert
boosted


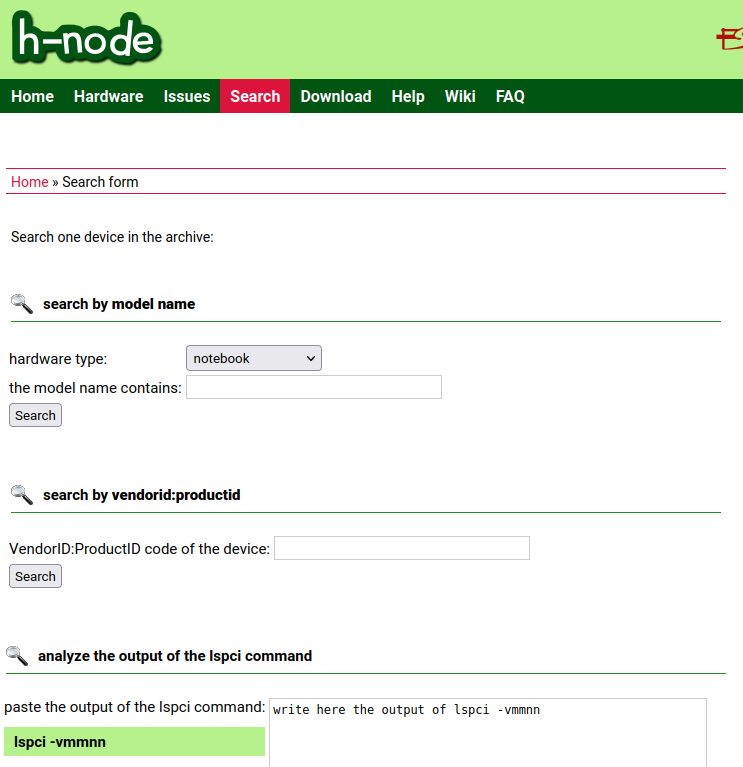
Need to know whether a piece of hardware is supported by free software? #hNode has you covered! Its search engine will help you verify #freesoftware compatibility. https://u.fsf.org/3uj
@bohemianchic@infosec.exchange Besides family and friends; learning, but sometimes the more you know the more depressing it gets.
@malwaretech I'd rather take less bandwidth trough any kind of cable (fiber, STP, whatever) than being forced through WiFi
- PGP
- 0x09208346d9245e65
- GitHub
- https://github.com/modrobert
- https://twitter.com/modrobert
- Bitcoin
- bc1qtxmtnc225p767x78k0xwcnhr0u64r655kqvc69
-"When the going gets weird, the weird turn pro..."
Joined Sep 2018
