

szescstopni @szescstopni@social.cleverlibre.org
Living in the #wetlands of #Polesia (also spelled #Polesie) in #EasternPoland. Surrounded by #bogs and #forests, trying not to fuck up surrounding nature too much.
Taking care of a small pack of #dogs – #IdąPsięta.
Luddite working with hi-tech.
#RuralBroadband provider by accident. Starting a small LoRaWAN project to monitor our wetlands. Coding in #Python. Dealing with dirty data, cleaning them when time allows.
#Atheist. I don't *believe* in #science – science is the *only* thing that protects us from belief.
Fuck nazis.
My account on Twitter is still up, for good reasons. https://twitter.com/szescstopni
I check facts before I toot.
I sometimes toot in Polish.
Zdolny, ale leniwy.
Joined Nov 2022
szescstopni
boosted

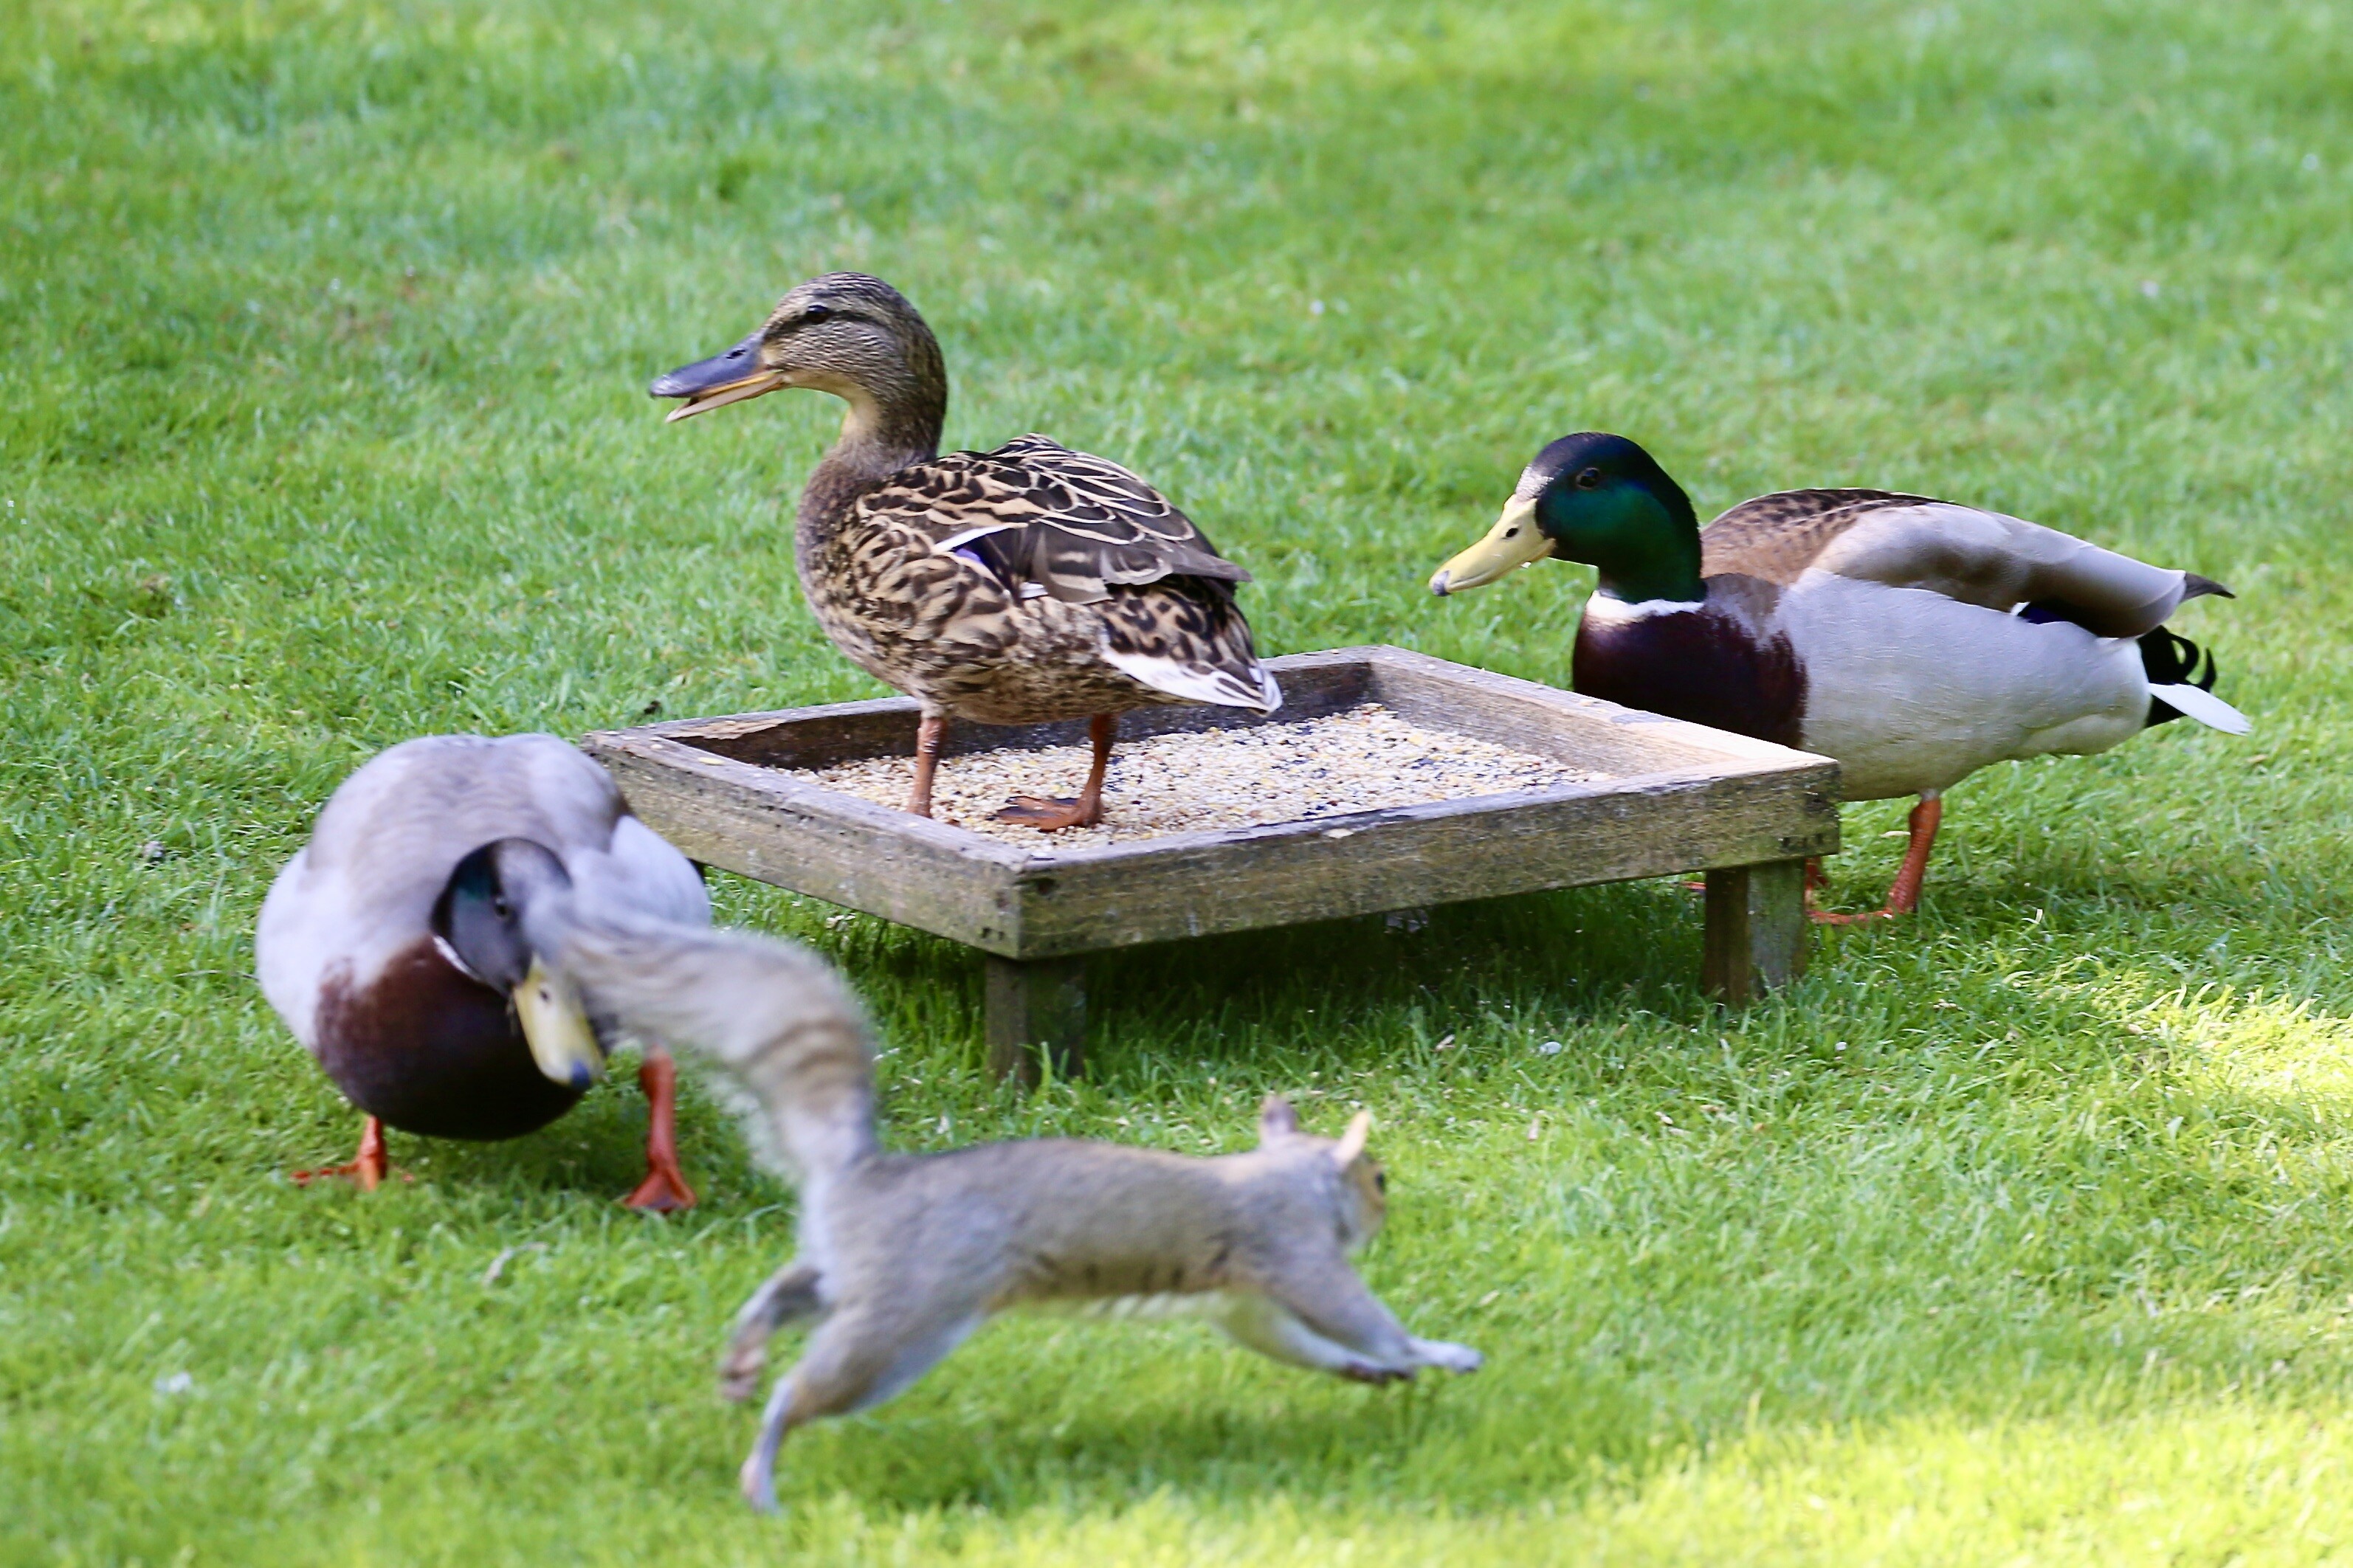
Bodyguard of the Princess in action 🦆 🐿️
#Ducks #Squirrel #Animals #BirdFeeder #Wildlife #Garden #Photography #Tiere #Enten #Eichhörnchen #Vogelfutter #Garten
szescstopni
boosted

szescstopni
boosted

"the probable cause was Columbia Gas of Massachusetts’ weak engineering management that did not adequately plan, review, sequence, and oversee the project.... NTSB issued the same recommendation and sent letters to the governors of 31 states with PE license exemptions, but most of those states still don’t require a PE stamp on natural gas projects today." https://practical.engineering/blog/2023/5/16/merrimack-valley-gas-explosions-what-really-happened
Do not go gently into the range of mobile reception. Stay in the forest.
szescstopni
boosted
I don't know what the squirrels in my back yard are up to *exactly* but I feel like I'm the one who's going to wind up in jail for it.
szescstopni
boosted

Menopause is incredibly rare in nature. Most animals die soon after their reproductive capability comes to an end. Aside from humans, only four species of wild animal are known to go through a form of menopause: orcas, narwhals, beluga whales and pilot whales. These animals might shed light on why menopause exists at all.
szescstopni
boosted

Ciekawa historia namierzania błędu, który ostatecznie okazał się krytyczną dziurą w kernelu #Linux :
https://dirtypipe.cm4all.com
szescstopni
boosted

#ThickTrunkTuesday #Photography #Nature #fungus #moss #Wettenberg
Mitten im Wald, im Krofdorfer Forst, ein zerfallender Baumstamm, von Zunderschwämmen besiedelt und mit Moos bewachsen. Photo von 2010

szescstopni
boosted

szescstopni
boosted

szescstopni
boosted

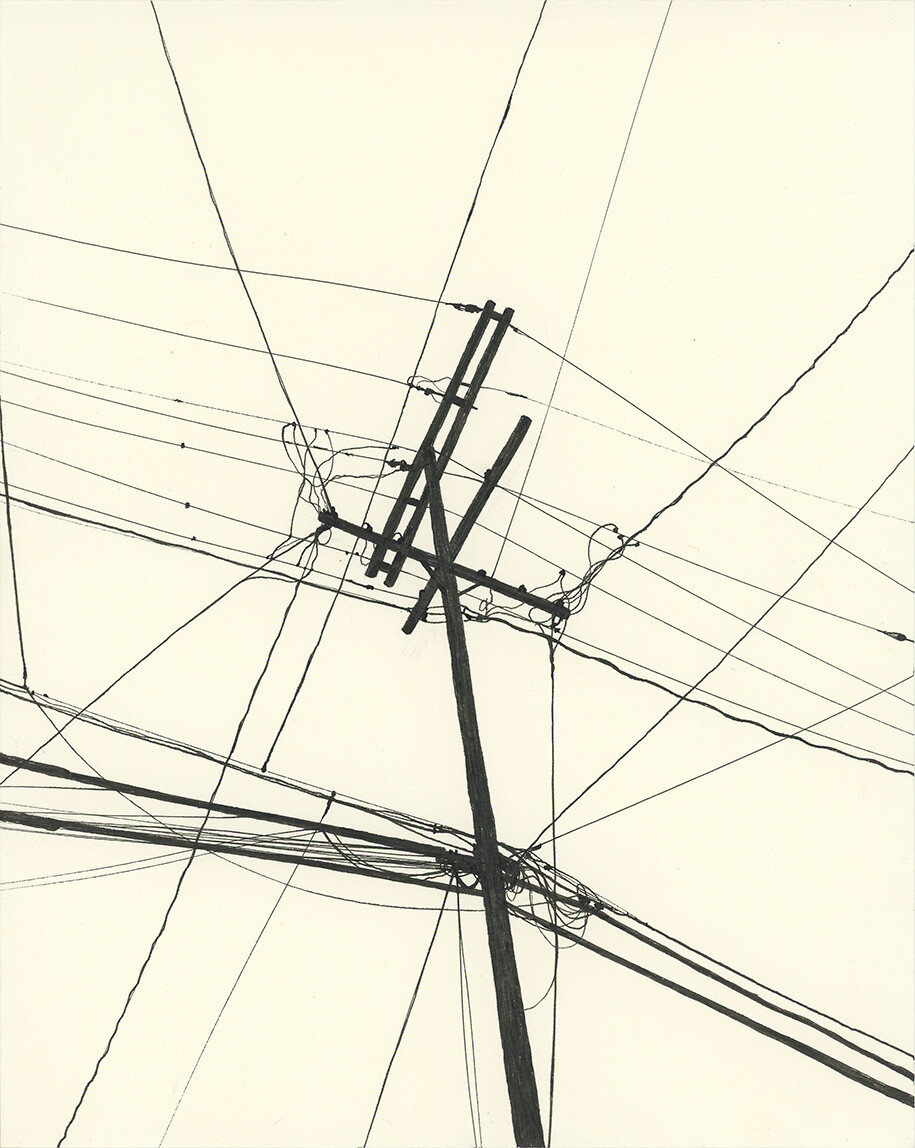
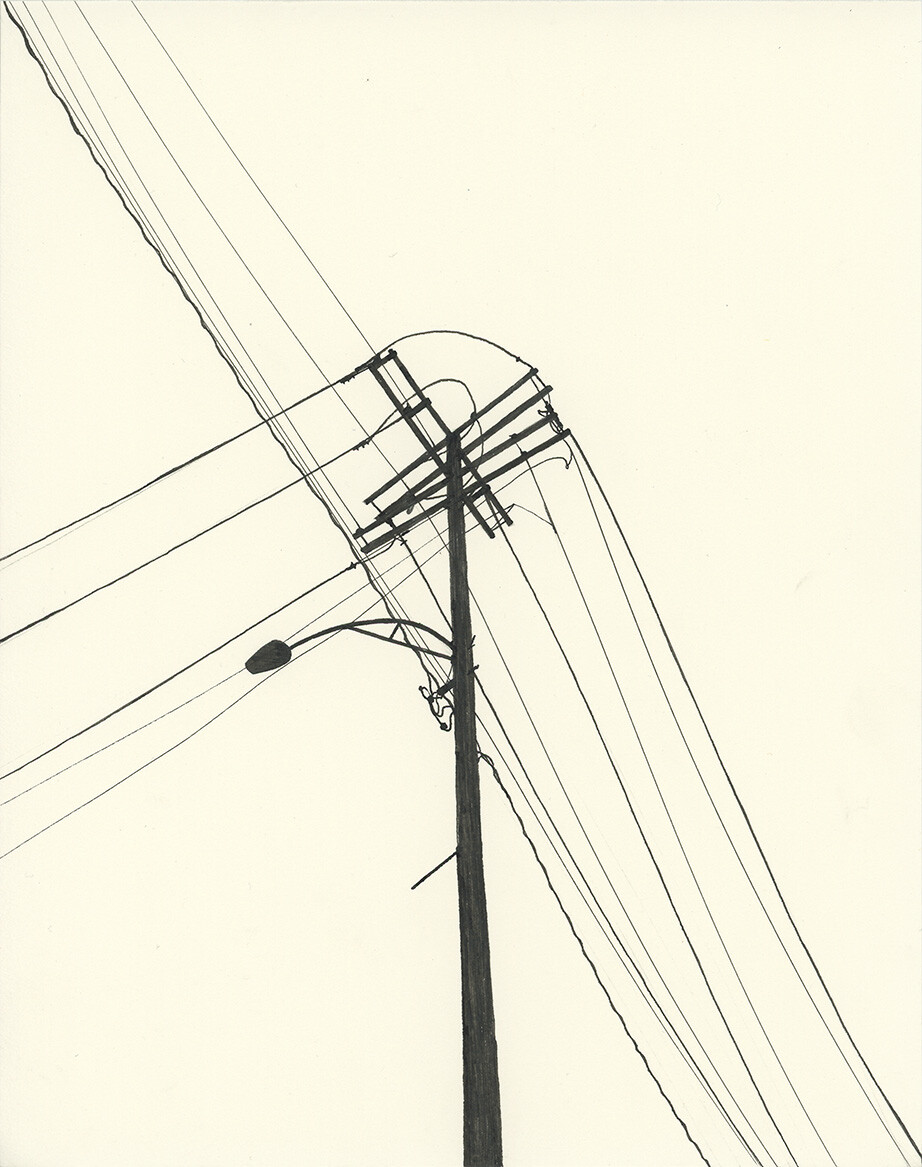
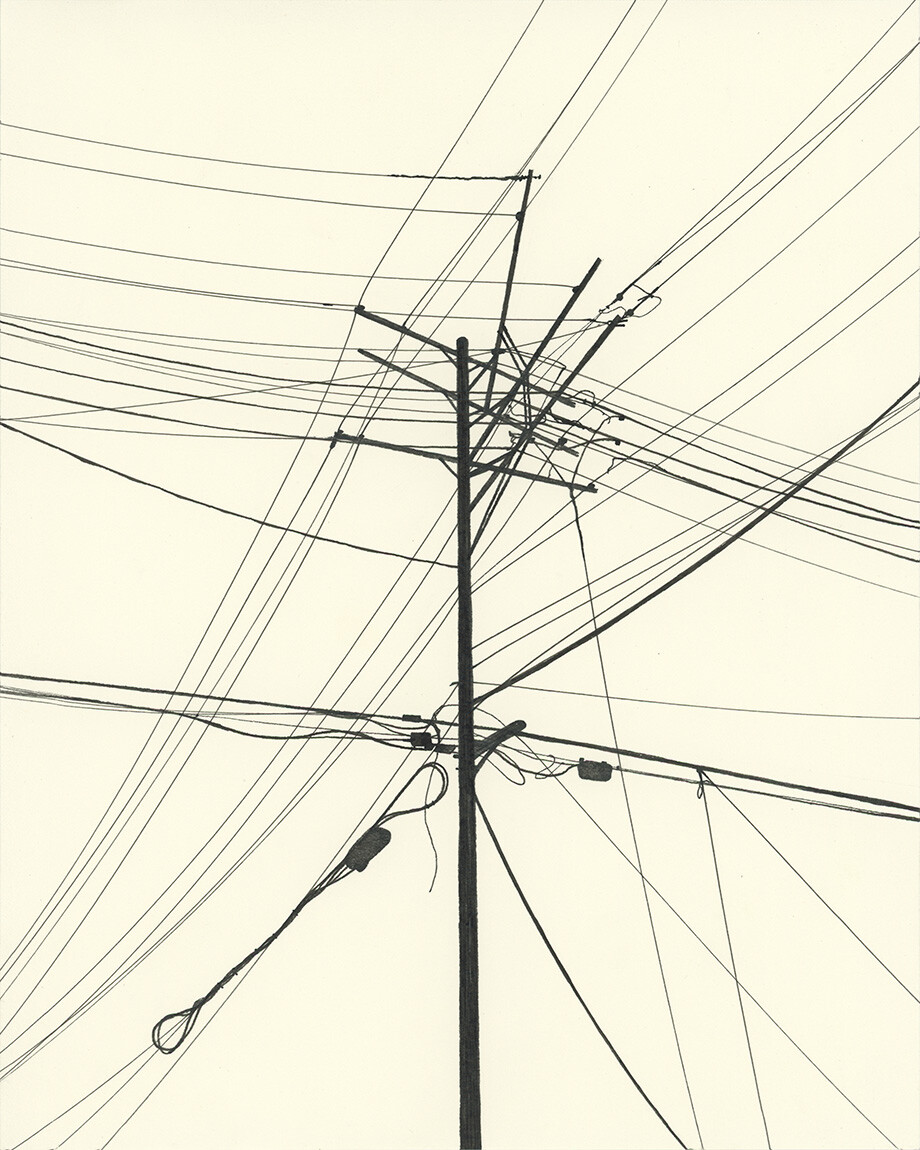
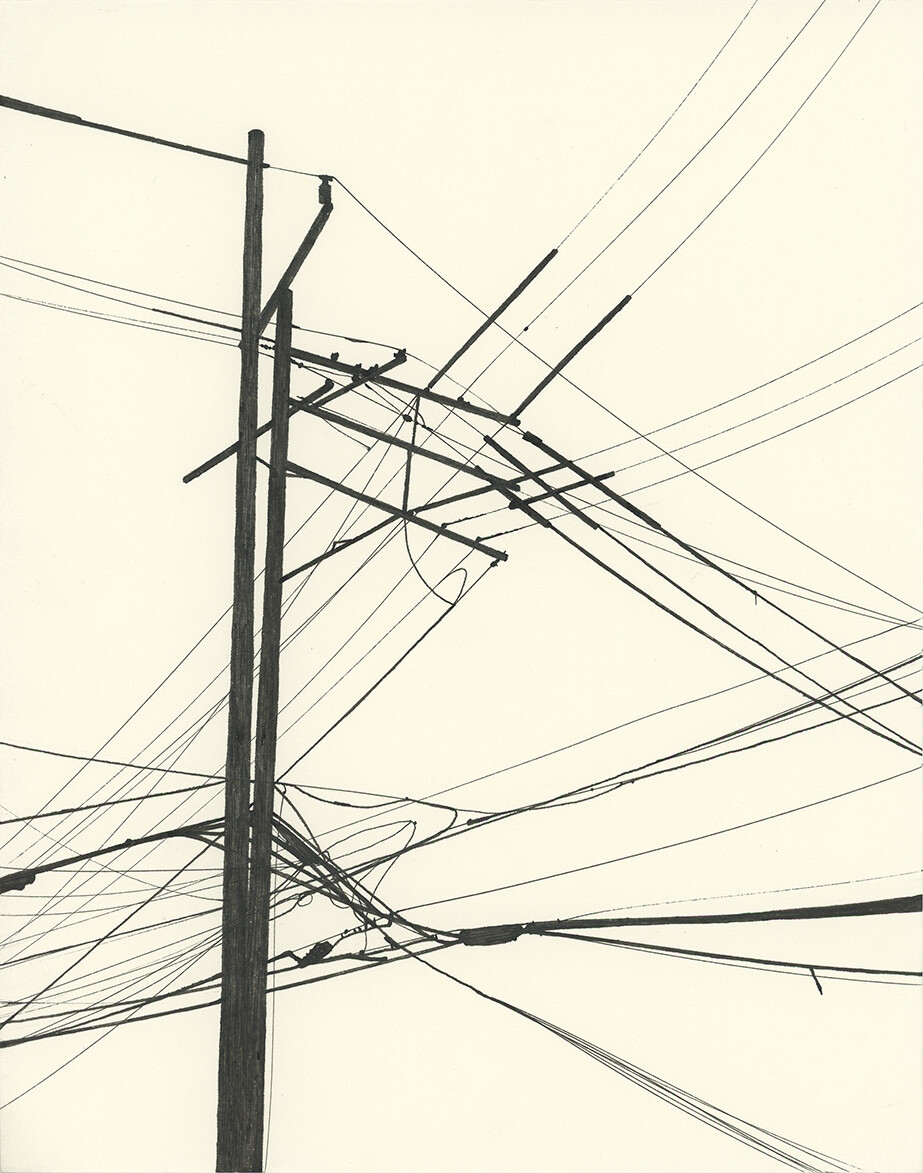
Here are some selections from my Power Lines Drawings series. [Pinned]
I draw these from clusters of power lines I see around me, primarily when I'm walking or biking around #Hamtramck or #Detroit.
Part of the point, for me, is the regular practice of walking/biking around the city and paying attention to the actual material of the built environment.
I've got a page with the whole series up here, updated as I draw them
https://marcusjmerritt.com/power-lines-drawings/
#ArtistsOnMastodon #MastoArt #drawing
szescstopni
boosted

@phrees Yes, my daughter has a Pentax k1000 someone was giving away. The counter stopped working and she was going to leave it like that until I mentioned maybe we can fix it. This manual https://pentax-manuals.com/markroberts/k1000_man.pdf and a screwdriver and that was it! Going through the manual is a reminder of how things used to be and how far we've fallen. Not only schematics in that manual but, step-by-step procedure for repair. We can fix the whole thing whenever we want on a camera built in 1976, 47 years later. #righttorepair
szescstopni
boosted

Brytyjczycy testuja 4-dniowy tydzien pracy z okresami, w ktorych w pracy nie odbieraja maili, telefonow / calli i ignoruja inne komunikatory
I jaki wynik? No niespodzianka - sa bardziej produktywni niz wczesniej - kto by sie spodziewal... 🙃
https://www.reuters.com/world/uk/making-four-day-week-work-britain-2023-05-16/
szescstopni
boosted
The surprising part is not that math grad students named Cox and Zucker would come up with the idea of writing a paper together just as a joke.
It's that they followed through after they were professors, and wrote a paper that was actually rather significant.
szescstopni
boosted

After reading the three The Register articles[^1][^2][^3] on the #CyberResilienceAct I have an impression that British press is again doing exactly what they have done on #Brexit - taking EU ideas their sponsors don’t like and intentionally distorting them to create an utterly absurd picture of “Brussels idiots”, while perfectly realising they’re lying. Just read this:
But the EU commissioners don’t have a clue about how open source software works. Or, frankly, what it is. They think that open source is the same as proprietary software with a single company behind it that’s responsible for the work and then monetizes it. Nope.[^1]
Note this is not written by some Daily Mail intern who doesn’t distinguish “directive” from “regulation”, this is written by an IT journalist who clearly has read the CRA draft. He perfectly understands what he’s writing about, he knows how the software market works. And then he writes this:
The CRA’s underlying assumption is that you can just add security to software, like adding a new color option to your car’s paint job. We wish! Securing software is a long, painful process. Many open source developers have neither the revenue nor resources to secure their programs to a government standard. The notional open source developer in Nebraska, thanklessly maintaining a vital small program, may not even know where Brussels is in Europe (it’s in Belgium). They can’t afford to secure their software to meet EU specifications.[^1]
I have spent quite large part of my professional life in software #security and I do #FOSS, so let me correct this misleading paragraph:
“Notional open source developer in Nebraska” may not have resources for user support and security, but doesn’t have, because CRA clearly excludes him from the regulation (preamble, item 10)
Because large companies still want to use the Nebraska library, and because large companies like to have “software support contracts”, they do pay for the latter to “software support companies” whose names we all know.
Majority of the “software support company” job is to repackage the original FOSS library and cash “support contract” payment. This is exactly how we ended with OpenSSL library being placed literally everywhere for decades until someone decided to have a look and found tons of vulnerabilities.
Could these vulnerabilities have been found earlier? Of course: the software (SAST, DAST, IAST etc) to do it is widely available. There’s just one problem: it’s bloody expensive.
Of course, Nebraska dev won’t spend 10^5 USD annual cost of a decent SAST scanner just for peace of mind. Otherwise, if someone sends a merge request with a fix, he or she will likely happily merge it.
But hey, maybe there’s someone in the food chain who is already casually cashing a lot of money for repackaging the Nebraska free software that could possibly spend a fraction of it for that kind of maintenance? 🤔
Make your own mind about who might be the most impacted by CRA here…
[^1]: https://www.theregister.com/2023/05/12/eu_cyber_resilience_act/ [^2]: https://www.theregister.com/2023/01/30/opinion_eu_foss_security/ [^3]: https://www.theregister.com/2022/09/16/eu_cyber_resilience_act/
szescstopni
boosted

Dear developers,
if you're outputting relative timestamps ("4 days ago"), please also include somehow the actual timestamp. The title-attribute in HTML would be a good starting point.
Yours truly,
a frustrated user looking for exact timestamps.
Our dogs, #IdąPsięta, playing "Wolves and Tourists"
szescstopni
boosted



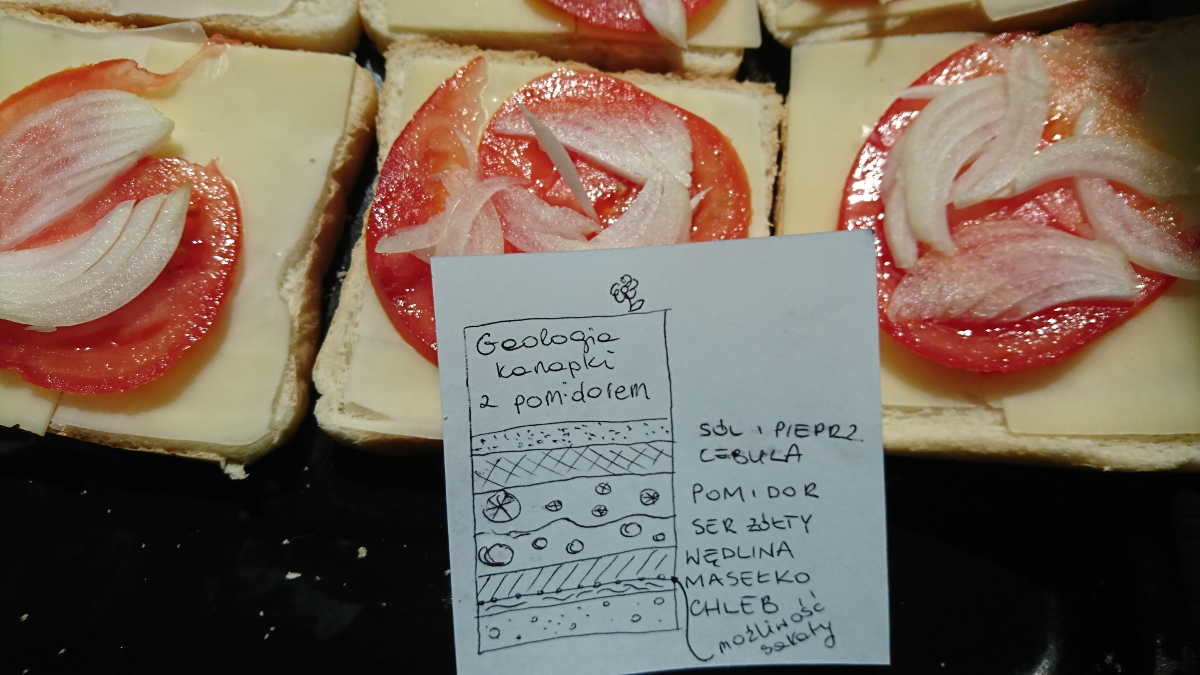




Są we mnie dwa wilki. Jeden kocha sernik. Drugi też
Living in the #wetlands of #Polesia (also spelled #Polesie) in #EasternPoland. Surrounded by #bogs and #forests, trying not to fuck up surrounding nature too much.
Taking care of a small pack of #dogs – #IdąPsięta.
Luddite working with hi-tech.
#RuralBroadband provider by accident. Starting a small LoRaWAN project to monitor our wetlands. Coding in #Python. Dealing with dirty data, cleaning them when time allows.
#Atheist. I don't *believe* in #science – science is the *only* thing that protects us from belief.
Fuck nazis.
My account on Twitter is still up, for good reasons. https://twitter.com/szescstopni
I check facts before I toot.
I sometimes toot in Polish.
Zdolny, ale leniwy.
Joined Nov 2022
