

szescstopni @szescstopni@social.cleverlibre.org
Living in the #wetlands of #Polesia (also spelled #Polesie) in #EasternPoland. Surrounded by #bogs and #forests, trying not to fuck up surrounding nature too much.
Taking care of a small pack of #dogs – #IdąPsięta.
Luddite working with hi-tech.
#RuralBroadband provider by accident. Starting a small LoRaWAN project to monitor our wetlands. Coding in #Python. Dealing with dirty data, cleaning them when time allows.
#Atheist. I don't *believe* in #science – science is the *only* thing that protects us from belief.
Fuck nazis.
My account on Twitter is still up, for good reasons. https://twitter.com/szescstopni
I check facts before I toot.
I sometimes toot in Polish.
Zdolny, ale leniwy.
Joined Nov 2022
szescstopni
boosted

Today's the day: The Ig Nobel Prize ceremony webcast starts at 6 pm US eastern time https://improbable.com/ig/2023-ceremony/
szescstopni
boosted

Yesterday I nearly bought a thermometer but realised just in time that it comes with an app. Oh hell no. I would like a much much stupider thermometer, please.
Hashtag not all software people or whatever, but I think it's funny that software people often hate software the most.
szescstopni
boosted

Uwielbiam rozmawiać z ludźmi, którzy są pasjonatami w swojej pracy. Niedawno miałem okazję odebrać swój rower z małego, lokalnego serwisu rowerowego obsługiwanego przez jednego człowiek. Pan, który to prowadzi, jest całkowicie oddany swojej pracy i widać, że po prostu kocha to, co robi. 😊
Czy też znacie takie osoby?
szescstopni
boosted

Gotta love the modern socialist talking point "Workers should be paid well and treated fairly, except for artists, who should make me all the stuff I like for free"
szescstopni
boosted


The MGM attackers claimed they used one of the easiest ways to breach/ransom a company, a method I use often in my hacking:
1. Look up who works at a org on LinkedIn
2. Call Help Desk (spoof phone number of person I’m impersonating)
3. Tell Help Desk I lost access to work account & help me get back in
While we wait for attack method confirmation, I’ll say that the attack method they claim worked for them does indeed work for me. Most orgs aren’t ready for phone based social engineering.
Most companies focus on email based threats in their technical tools and protocols — many are not yet equipped with the social engineering prevention protocols necessary to catch and stop a phone based attacker in the act. Teams need protocols to verify identity before taking action.
The 1st teams I go after when hacking are the folks who deal with requests from people constantly — IT, Help Desk, Customer Support, etc.
I often pretend to be an internal teammate to convince them to give me access, and I usually start with phone attacks bc they work fast.
Email phishing attacks can get caught in good spam filters and reported.
The soft spot for many teams are the folks who handle the phone call requests.
There’s a perfect storm: lack of verification protocols, easy spoofing, compensation tied to how fast they handle requests.
Questions to ask internally to see if your team is prepared to catch this attack:
- Do the folks who handle requests from team/customers use identity verification protocols?
- Do we rely on knowledge based authentication? DOB + caller ID matches ☎️ number in system, for example.
- Are our IT/Help Desk/Support teams compensated or promoted on the speed of saying yes to requests? Have we incentivized time for security protocols in Support?
- How do we verify identity first?
Remember, most folks at work want to do a good job and often times “good work” means “fast work”. We can’t expect every employee to be able to come up with their own identity verification protocols on the fly — it’s our job to provide the right human protocols to catch this fast.
We’ll need to wait to learn the details of the attack and get confirmation.
In the meantime, I can tell you I compromise orgs w/ the exact phone attack the attackers claim to use and many orgs don’t have phone call based identity protocols to catch it yet.
Update your phone based identity verification protocols to catch account takeover attempts!
You know your org best & there’s no one size fits all.
You can move from KBA (like DOB) to OTP on 2nd verified comm channel, call back to thwart spoof, service codes, pins, and much more.
After hacking & educating orgs on how they can catch me, the biggest task I spend my time on is updating verification protocols to spot me next time. It’s maddening to get caught on their new identity verification protocol on the next pentest but there’s also nothing I love more.
More details here: https://x.com/RachelTobac/status/1701801025940971792?s=20
@unofficial_kbin_guide Hi. A very useful guide. What is its copyright status? I was thinking of getting it translated into Polish.
szescstopni
boosted

Things nobody tells you about being homeless:
1) Almost nobody gives a fuck about you if you're homeless. It is seen as a personal failing. It is never seen in a wider context.
2) Not even homelessness assistance agencies give a fuck about you if you're working homeless.
3) Not even leftists aid orgs give a fucking damn about you unless you're not working and you're on the street. Believe me, I tried. They don't care about the working homeless or those who just need a hand up.
4) Pretty much all the homelessness aid that does exist is for addicts on the street.
5) Unless you have friends or family with money, nobody is going to help you escape being stuck in extended stay hotels, which often cost so much you can't get out of them, by design.
6) It is very expensive to be homeless as everything costs far more. Washing clothes, showering, eating, etc. all become very expensive. Even transportation becomes more expensive sometimes, if you're stuck taking taxis or Uber.
7) Virtually all homelessness aid assumes you don't have anyone else with you. If you've got kids or a partner, good luck getting help for them, too.
szescstopni
boosted

How the illegal harvesting of giant trees in California shines a light on rural poverty
szescstopni
boosted

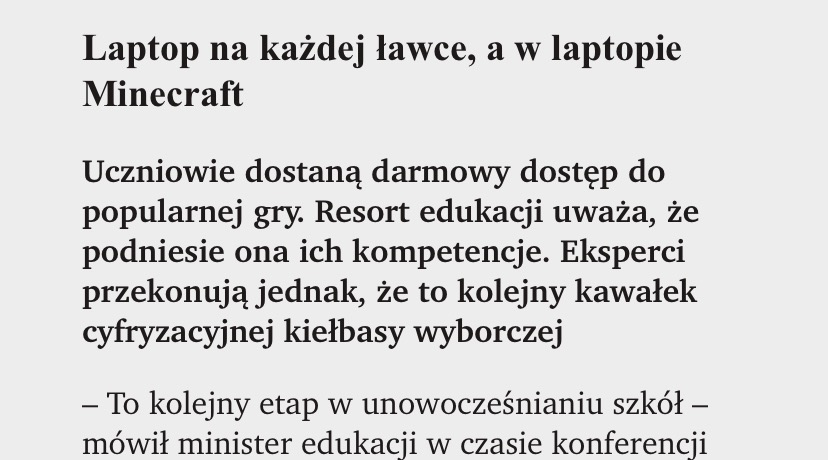
Kolejny element rozwoju - darmowe laptopy dla uczniów do grania w gry, za miliard PLN? W niewielkim stopniu zwiększy kompetencje u młodych. Albo w żadnym.
A te są niższe niż u starszych generacji, zmuszonych do kompilowania kerneli. Mimo tego że wychowali się od urodzenia z komputerami smartfonami, internetem.
szescstopni
boosted

Hey guys! I've spoken a few times about the wonderful people behind the So Farscape podcast, and now that this has ended, they are starting a new project! For those who are curious, here's the trailer for what they're doing next!
* The Joy of Trek
Two lifelong besties (and their trusty engineer) adventure through the vast constellations of Star Trek's decades on TV, especially the lesser-loved stories.
But instead of bitching about why they’re bad, we’re going to find the joy in each of them because everybody loves the great episodes, but it takes dedication, insight, and hard-working fools to love the clunkers too.
And by Jove, we are those fools! Positive, inclusive and optimistic (though not uncritical!), we try to find the brilliance even in the least-loved episodes of our favourite TV shows!
Coming later this year. You can subscribe at https://joyoftrek.com/listen if you want to be sure to catch it when it drops.
--------------------
#farscape #sofarscape #startrek #rss #podcast #scifi #fun
Cast:
K : @sable Khaki : @khakidoggy
Trusty Engineer: Greg (no presence on Mastodon yet, afaik)
--------------------
Please help my dear friends by giving this a boost, and I hope you'll join them on their adventures!
szescstopni
boosted

Common Grackle at the bird bath, gripping the edge.
Nikon z6ii, 700mm, ISO 4000, 1/500s, f/8, handheld.
#BirdPhotography #BackyardBirding
szescstopni
boosted

@MediumWasTedium some years ago we took a teenager to a classic car thing (Petaluma's Salute to American Graffiti), and, as he smelled the unburned hydrocarbons of carbureted engines, he asked "did the past really smell this bad?"
So, yeah, gasoline, too.
szescstopni
boosted

This week I went to an event where they had this amazing machine that demonstrated the workings of a heat pump: taking a unit of heat from the right side and transferring it to the left side, the beers are cooled and the (vegan) sausages are warmed. I think it's brilliant and should be used to overcome any doubts or resistance to heat pumps, especially in Germany. Maybe they should be mandatory in every beer hall?
szescstopni
boosted

Znany lewacki szmatławiec *sprawdza w notatkach* Tygodnik Powszechny znów znów się przypiertala do miłościwie nam panujących ojców narodu.
https://www.tygodnikpowszechny.pl/ustawa-dla-bogatych-w-polsce-rodzi-sie-oligarchia-184581
Link bez paywalla:
https://12ft.io/proxy?&q=https%3A%2F%2Fwww.tygodnikpowszechny.pl%2Fustawa-dla-bogatych-w-polsce-rodzi-sie-oligarchia-184581
szescstopni
boosted

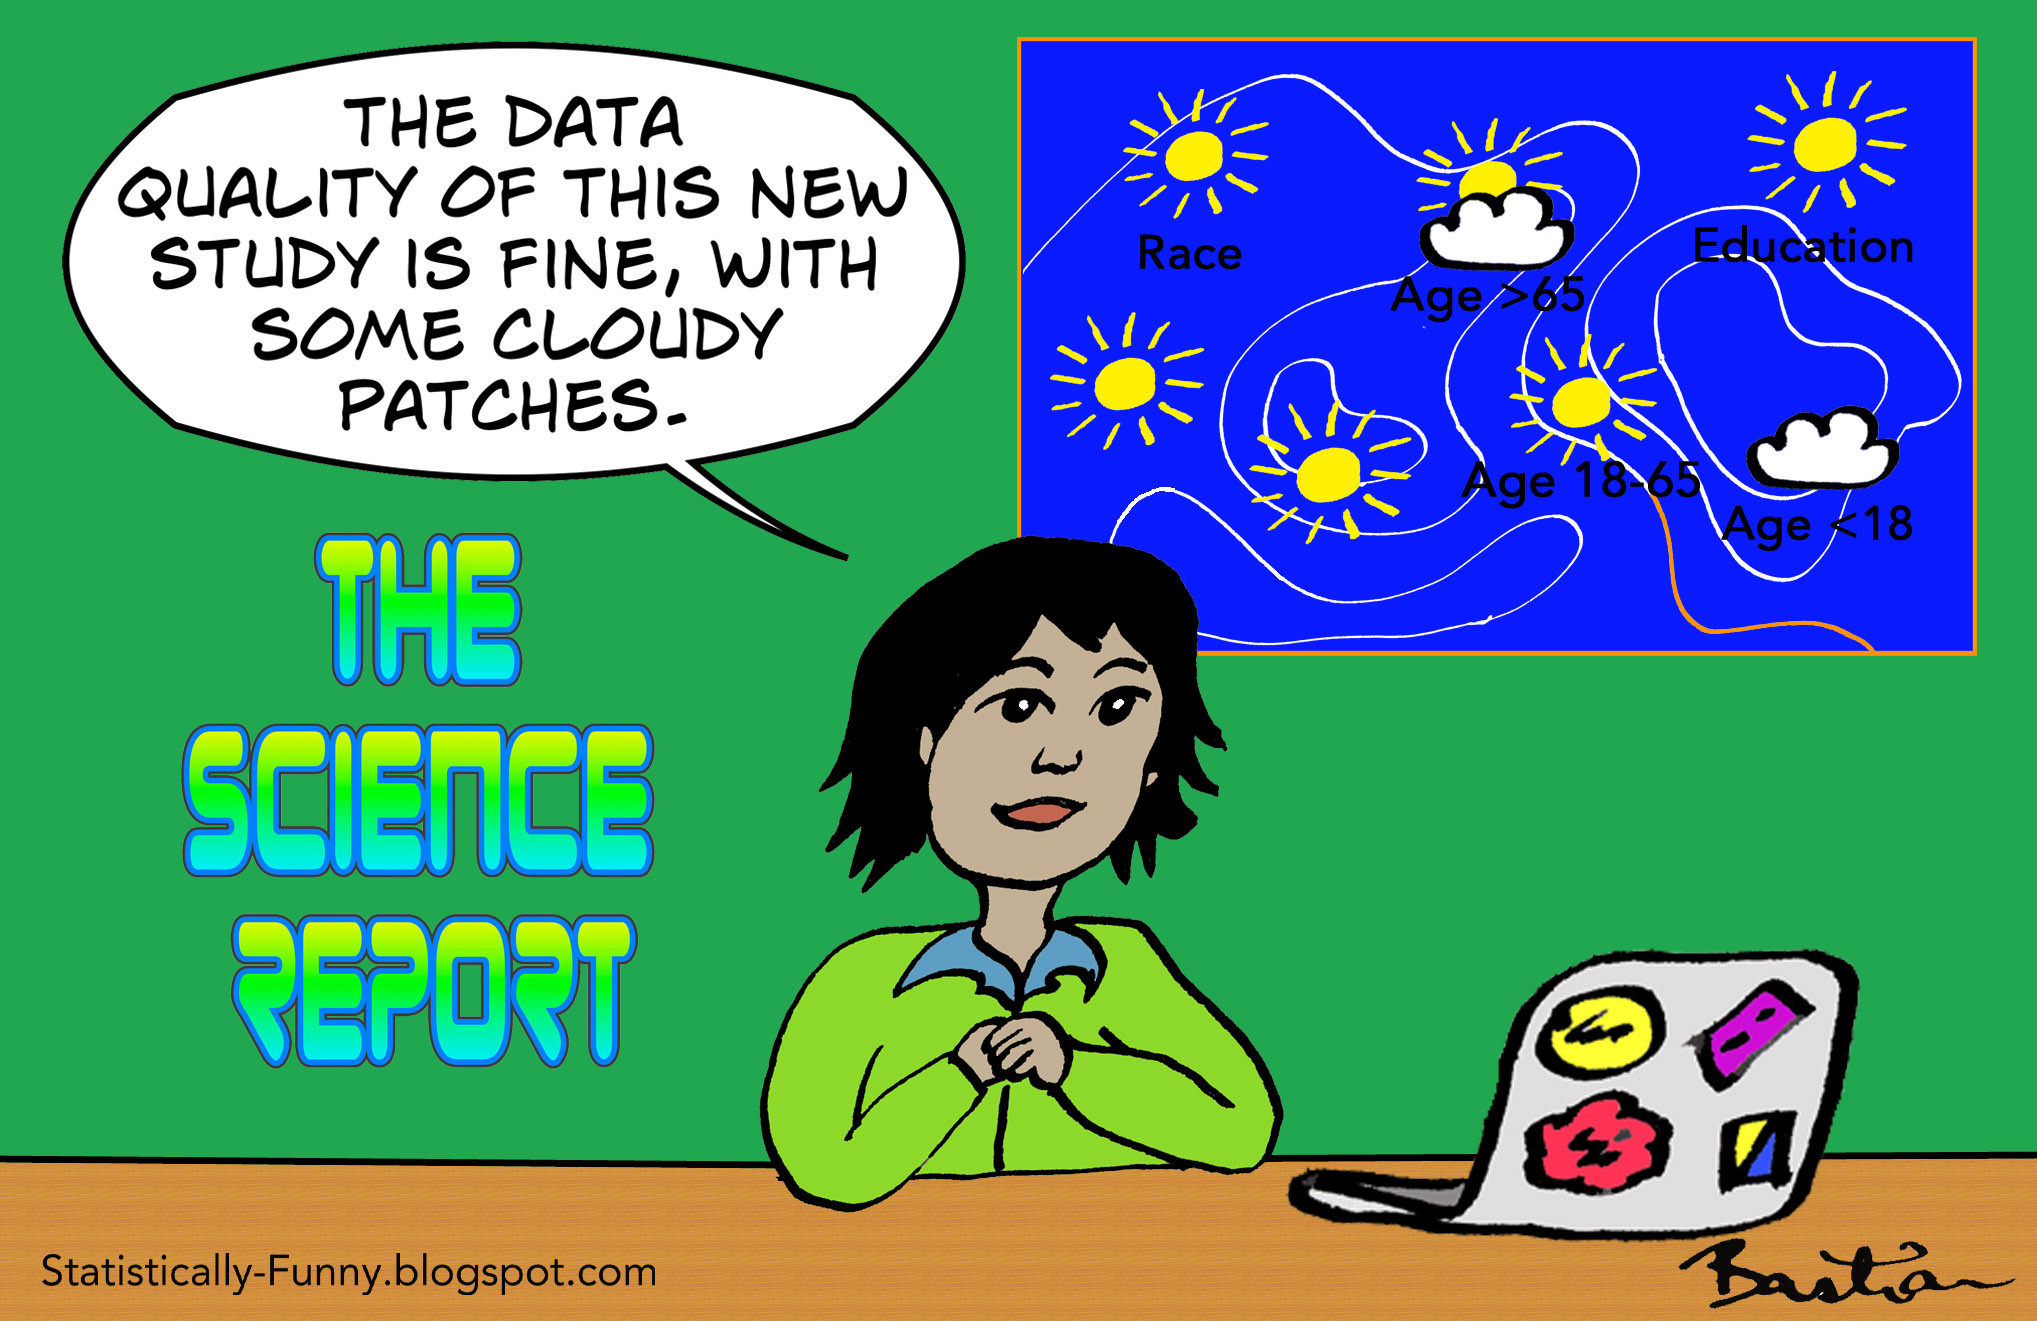
"It's a good study" - that can be a trap! The quality of results vary within a study, & it mightn't be reliable for every question - or even the most important one.
From this old post: https://statistically-funny.blogspot.com/2016/09/the-highs-and-lows-of-good-study.html
szescstopni
boosted

"We don't need to visit Egypt, we've got Suez at home."
Suez at home:
szescstopni
boosted

@dalias Generative #AI “a DDoS attack on written knowledge.” That’s a brilliant metaphor, and a very apt one, I think.
Remember the “grey goo” we worried about with nanotechnology, where there would be so much replication of these thing that it would flood the streets with their endless copies? Like the paperclip replicator.
What we are seeing is virtual grey goo oozing everywhere online new.
szescstopni
boosted

Is Kbin dying? I wanted to address the deleted thread and provide some insight into the current situation.
/kbin is certainly not dying, as @fr0g pointed out, work on new features and bug fixes is ongoing. However, it may give the impression that it is, and for that, I take full responsibility and owe you an explanation.... #kbinMeta https://kbin.social/m/kbinMeta/t/451896
szescstopni
boosted

Kiedyś znajoma zaczepiła w co tramwaju nastolatkę z bluzą z napisem "Nirvana" - i usłyszała od niej, że to "taka fajna firma odzieżowa" (sic!)
Teraz widzę coraz więcej ludków w ubraniach "Tupac".
Ciekawe, renesans starego rapu czy kolejna "fajna firma odzieżowa"?
szescstopni
boosted



Nice sub-woofers!

Living in the #wetlands of #Polesia (also spelled #Polesie) in #EasternPoland. Surrounded by #bogs and #forests, trying not to fuck up surrounding nature too much.
Taking care of a small pack of #dogs – #IdąPsięta.
Luddite working with hi-tech.
#RuralBroadband provider by accident. Starting a small LoRaWAN project to monitor our wetlands. Coding in #Python. Dealing with dirty data, cleaning them when time allows.
#Atheist. I don't *believe* in #science – science is the *only* thing that protects us from belief.
Fuck nazis.
My account on Twitter is still up, for good reasons. https://twitter.com/szescstopni
I check facts before I toot.
I sometimes toot in Polish.
Zdolny, ale leniwy.
Joined Nov 2022
