Void Abyss @voidabyss@social.cleverlibre.org
Joined Aug 2021
@Albert_Hubble
> What is your solution to this if going for green electricity and green fuels isn't the way?
in the short term natural gas (cleaner then diesel fuel) can be used to power shipping vessels. https://www.econnectenergy.com/articles/how-do-lng-ships-work
Renewable energy used directly to supply the electric grid reducing coal and gas/fuel powered stations, mid to long term deploying small nuclear electric power stations replacing gradually fossil fuel power stations(see France as example).
The energy transition need to happen gradually and using technology that is robust, efficient and cost effective. Drastically cutting fossil fuel, just create inflation, food starvation and societal turmoil.
I am pretty sure that green hydrogen will have some industrial application for reducing carbon emissions, but as an energy storage it's not efficient nor cost effective no matter how much the polluter industry want to promoted and green washed.
@Albert_Hubble That's called greenwashing and you didn't bring any scientific argument other then parroting Maersk's marketing material.
Don't take the big polluters words at face value and go look up scientific facts and research.
> But, for now, many of the companies pushing hydrogen aren’t doing so to save the planet. They’re doing so to save their business models in a time of extreme transition towards greener technologies and e-mobility.
@empiricism Is it just me or both links don't work?
@0 Most of legacy media are done and they know it.
> It's all very good to talk and disinformation, propaganda, fake news, etc, etc, etc.
This is their last-ditch effort to give themselves legitimacy while most people know their bias and they are the source of propaganda and disinformation.
The future of news media would be a combination independent journalists with crowd sourcing fact checking news distributed throughout social media monetized with a subscription/donation model (Substack/Patreon).
Void Abyss
boosted

Poll: How many parked domains do you have without any project attached (you are just paying renewal fees)? Please boost it so that wider dev/IT community can vote it. TIA.
Void Abyss
boosted

Hmmm. Another flavor of #pleroma, but with a fresh look. https://soapbox.pub/2022/12/25/releasing-soapbox-3-0/
Moderately easy to install, but having to rebuild Elixir stuff is a pain, and media attachment handling seems undocumented (At scale, at least). Still, it’s cute.
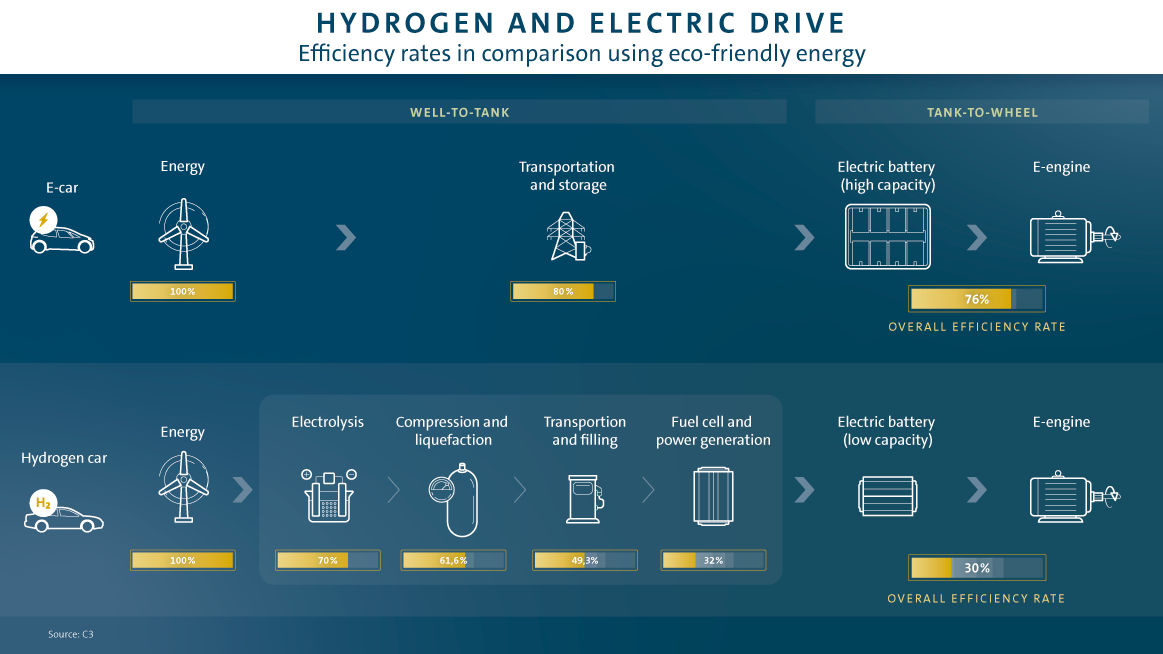
@Albert_Hubble @TatianaIlyina How is producing **Green hydrogen** any efficient or cost effective?
It take either Natural gas or ultra clean water(highly in demand) plus a of of energy to produce hydrogen.
Its overly complicated/costly to store and transport and then to converted back to energy it's an overall efficiency of 30%
@TatianaIlyina It's really not that's just a mass psychosis illness that drives some people to make that cheap short cut and deceitful association that CO2 = climate change.
There are many factors that play in climate change, human factor play a role in it for sure and to reduce our impact, let start by reducing/cutting mass manufacturing of garbage one time use plastics products(toys, tools, packaging household items etc..), toxic chemicals and
products with programmed obsolescence.
Lets reduce waste and promote long file cycle products, repair and recycling.
There is some much area to improve and reduce mass consumption therefor reducing fossil fuel energy demand without the disruption of civilization.
This obsession with cutting fossil fuel won't solve any climate change problems it's just creating turmoil in society were the poor suffer the most with the rising food cost
inflation.
I am more and more start thinking that the intended consequence of the climate change movement is the destruction of civilization. e.g. Sri Lanka. The **drastic** cutting of fossile fuel leads to food shortage which leads to mass starvation and societal turmoil.
Less humans = no climate change.
@0 @zeab
I don't think it's related to that protocol, it's more so the implementation of E2E encryption in #Matrix https://matrix.org/docs/guides/end-to-end-encryption-implementation-guide
This issue is overly complicated and it shows up in different forms.
This is closest of what I had experienced
https://github.com/vector-im/element-web/issues/23381
@zeab #Matrix
sucks so much it's unbelievable!
I can't read an encrypted message sent to me when I was logged out and that's normal for some #matrix devs, they think that improve security for some reason. And don't get me started how slow loading some rooms are and some times they don't load at all.
#xmpp protocol it's good, I like the #movim project https://github.com/movim/movim
But I don't know how much trouble to manage/admin an #xmpp server yet.
@0
> And, btw, why in this day and age do Western countries have "single sex spaces"?
Are you ok for penised individual sharing changing room naked with your teenage uterus carrying son/daughter?
@empiricism
What do you mean by?:
> adults go "blah blah blah"
As far as I can see, some politician and corporations uses "environmental science" to get big gov funding and they don't care at all about the environment, there is a lot of deception in that environment (pun intended) and scams going on since the 70s!
Here is Greta 1.0 speaking at the UN in 1992
https://www.youtube.com/watch?v=JGdS8ts63Ck
@aven Thank you for sharing the information for you used for the repair, I would like to learn electronics as well and I think the best place to start is tinkering with repairs 🙂
@Effortless@noagendasocial.com there is no dog bastard!
@toiletpaper it's ridiculous at this point, no one believe their propaganda anymore, everyone knows the vax don't work and there are many vax injured, excess death, worsening health conditions but lets forget all of that and give big pharma billions of tax money to keep this madness going!
@DrJackBrown Poor women used in a political chess game.
@mrman you got me!
Void Abyss
boosted

LASTPASS NEWS ALERT AND COMMENTARY:
LastPass attackers know your name and billing address and all websites you have saved passwords for, and if your master password isn't sufficiently strong may be possible to brute-force open everything on attacker's machines.
PLEASE READ BEFORE PROCEEDING: https://blog.lastpass.com/2022/12/notice-of-recent-security-incident/
The fact LastPass doesn't encrypt website URLs is a known flaw it appears they never fixed on purpose, going back almost 6 years:
https://hackernoon.com/psa-lastpass-does-not-encrypt-everything-in-your-vault-8722d69b2032
This eventual possible security breach was planned-for as part of LastPass' design for username and password protection. This doesn't break the core offering.
But it has stripped away multiple layers of protection and will hasten my looking at @bitwarden
It's impossible to be completely secure in a massive offering. However I have always disagreed with their decision to not 100% encrypt all metadata, and this event shows that was a foolish choice when seen against the inevitable of the entropy our complex electronic systems.
In the end, a password manager is still right choice in comparison to alternative. And a cloud-native offering like LastPass strongly hedges against data loss by normal users trying to manage their own vault. That is an undersold primary risk, not hackers. Still, very disappointed.
Current password setup:
- Primary vault is LastPass with 2FA
- Core fallback "key" accounts like email that allow pw reset are only in a KeyPass db file with 20char password, synced via OneDrive+2FA.
- This is then further backed-up with BackBlaze, using 40char encryption key
@darth
The #fediverse is still at its infancy, some admins want to overprotect and nanny their users other admins want to provide wide reach, free speech and tools for better user experience.
In the end, instances that share the same values of openness, transparency and accountability will naturally keep the federation others that want to be overprotective, imposing block lists upon other instances will remain isolated in their bubble.