
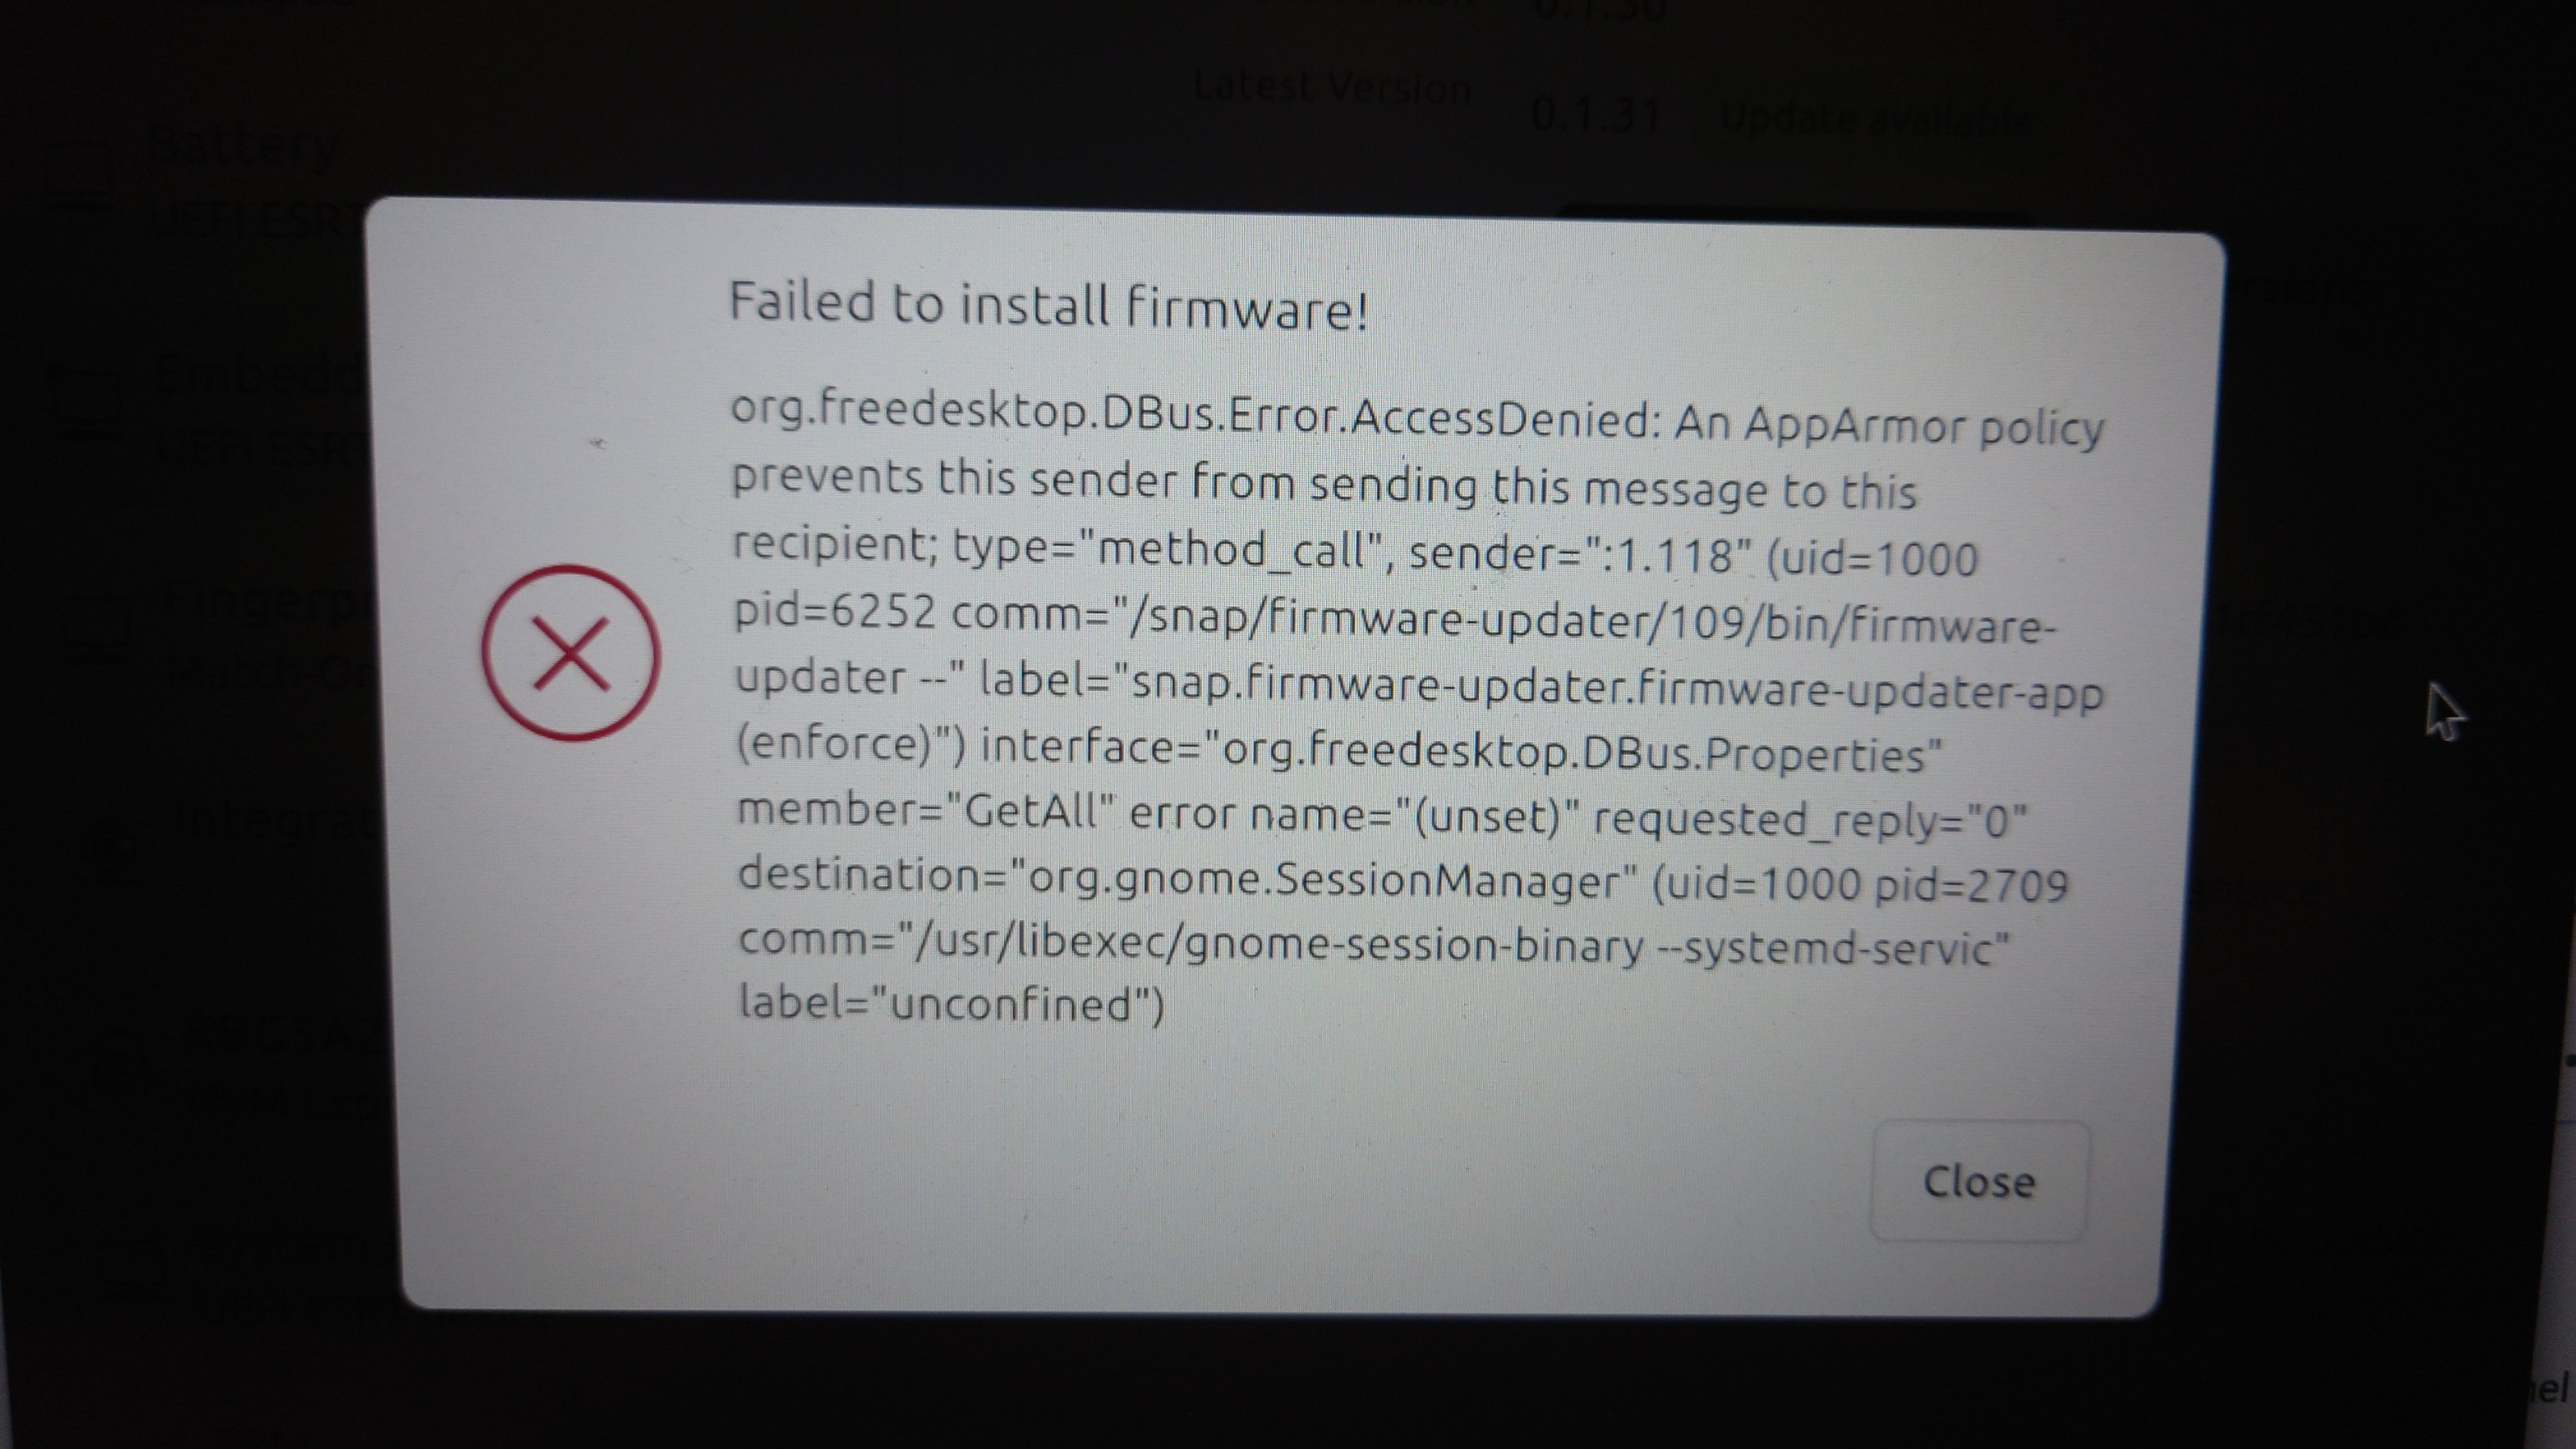
GOOD: Ubuntu 23.10 has AppArmor policies in place to prevent arbitrary executables from performing updates to my laptop firmware
BAD: Ubuntu 23.10 did not put in place exceptions to their AppArmor policies, nor a GUI path for the user to escalate privileges and bypass the AppArmor policies, in the firmware-updater app which Ubuntu itself jnstalled
VERY BAD: After getting the above error message explaining it was not going to allow me to update the firmware, I got a second dialog warning me not to turn off the computer while the firmware is installing, implying Ubuntu's firmware-updater app is written in such a way it does not understand the idea that one of its operations could possibly fail (for example because of security measures introduced by Ubuntu).

@mcc that seems to be a serious pattern in this release. so many times the so-called security features break it beyond usefulness. (“so-called" because then people fix it by just disabling all security.) same when i installed deb versions of firefox & 1password and they *still* wouldn't talk - turned out to be apparmor (1password support helped diagnose this). that's when i bailed to fedora (39). where it all just worked.

@mcc @StrangeNoises hmm. That's using LVFS which is the defacto standard .. ? Or some other Snap'd thing?

@falken @StrangeNoises If I run `which firmware-updater` I find it is in /snap/bin/firmware-updater. I do not have in my notes that I specifically installed this, and it's not listed in the Snap Store, so I assume it was installed by default when I installed the distro. I don't know how to get a better diagnosis of what the app s or does..