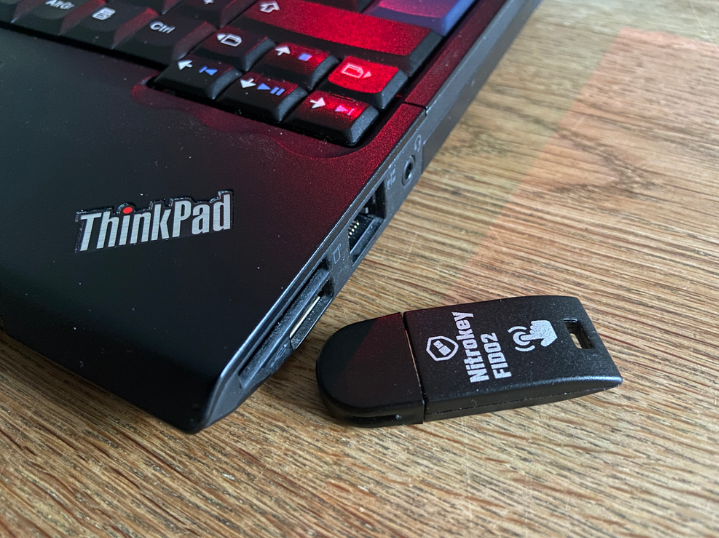
Now my #Fedora requires this #FIDO2 key to open LUKS on boot, login in gdm and sudo on terminal. Pretty nice hardware from @nitrokey

@exfil Well done! Do you share your config files somewhere, because I am interested how you did it.

@oxo
# LUKS Setup
# Check luks details of your drive
cryptsetup luksDump /dev/sda3
# Enroll fido2
systemd-cryptenroll --fido2-device=auto \
--fido2-with-client-pin=true \
--fido2-with-user-presence=true /dev/sda3
# Modify /etc/crypttab
luks-xxxxxxxx-xxxx-xxxx-xxxx-xxxxxxxxxxxx UUID=xxxxxxxx-xxxx-xxxx-xxxx-xxxxxxxxxxxx - fido2-device=auto
# Regenerate initramfs
dracut --regenerate-all --force

Sign in to participate in the conversation
CleverLibre Social

CleverLibre Social is an inclusive social instance for open discussion, learning, and community.
All cultures welcome.
Hate speech and harassment strictly forbidden.