
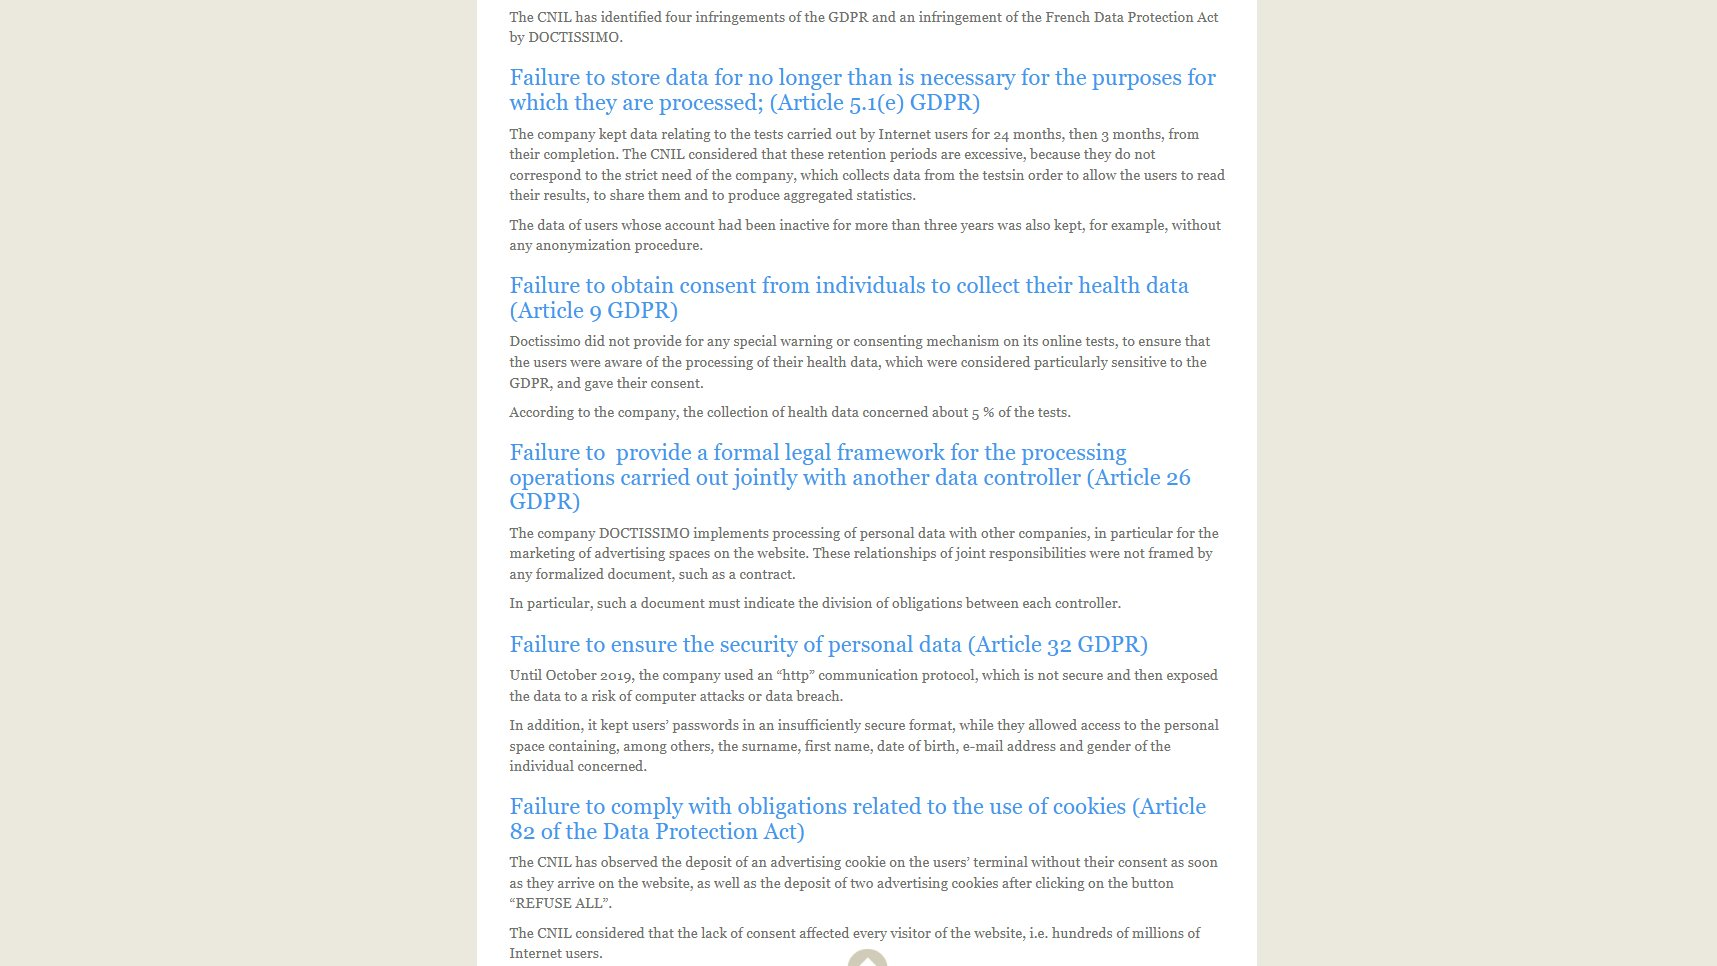
The French data protection authority CNIL fined the French health website http://doctissimo.fr €280k for GDPR infringements plus €100k for ePrivacy infringements:
https://www.cnil.fr/en/health-data-and-use-cookies-doctissimo-fined-eu380000
This is good, but. A few comments.
It's good they took action against a web publisher, which European regulators rarely do.
And the fine may represent a considerable amount of the site's revenue (according to internet sources). It's still not much for Reworld Media though, which appears to own the site.
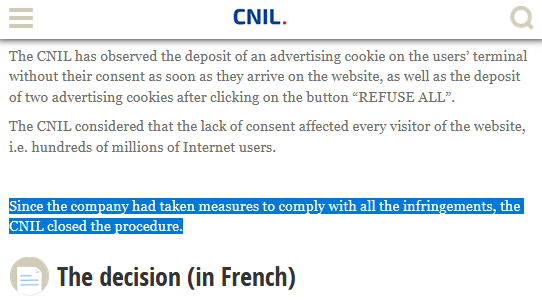
I understand that regulators have to focus on certain issues. However, closing the procedure with the argument that "the company had taken measures to comply with all the infringements" is not ideal.
This makes it look like everything is fine now, which may not be the case.
There are several unresolved GDPR issues regarding digital tracking.
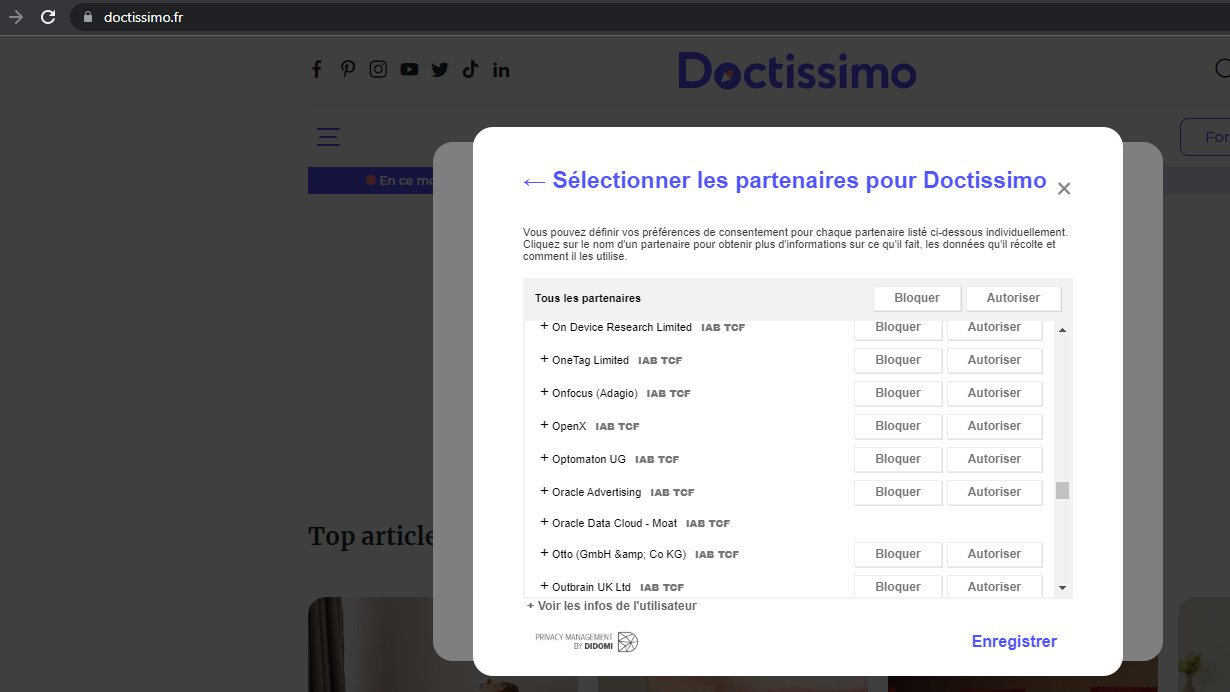
While doctissimo at least implements the very minimum (top level 'refuse' button), it still uses the TCF and wants users to 'consent' to personal data sharing with ~700 third parties, many of them data brokers.

The problem is you mention things like this to people and you just get fobbed off. The problem is serious, but no one seems to want to listen.
