

 bonifartius 𒂼𒄄
@bonifartius@social.cleverlibre.org
- woke?
- bespoke!
- problems?
- yes, many.
- ,.-~-.,.-~-.,.-~ <°((((((((((>< ,.-~-.,.-~-.,.-~
- ,.-~-.,.-~-.,.-~ <°((((((((((>< ,.-~-.,.-~-.,.-~
- pronouns?
- sure, nouns are nice
state licensed lolbert and hypernatalist with a breeding kink. never watched rick & morty and i'm proud of it.
don't only rely on my words, read what happy customers wrote about me: "10/10 would buy again", "top seller, great value", "wildly incorrect", "teil des problems", "without imagination", "Repeated provocation using copy/paste.", "if you take a dump in my mentions, I just might notice the smell", "log out and never login again", "Du redest wirr.", "My brother in Christ, this is such a ridiculously dumb statement that I will no longer entertain this silly conversation.", "Auf Derailing-Diskussionen habe ich keine Lust. Finger über dem Blocken-Knopf.", "Wie gesagt, du kannst der Diskussion inhaltlich nicht folgen."
➡️ NO PRESSURE ⬅️ 💄NO DIAMOND💍
one day at a time.
Joined Jun 2020
bonifartius 𒂼𒄄
boosted
 bonifartius 𒂼𒄄
boosted

 b e a r d
bonifartius 𒂼𒄄
boosted

Just hear now Portugal is using pcr "tests" again 
bonifartius 𒂼𒄄
boosted

From time to time I get shown pictures of my family and loved ones taken w cellphones. It's like looking at a funhouse mirror. Huge, distorted heads; A caricature of the person I know. "What a nice picture, huh?" They ask me. I'm perplexed.
Sometimes I point it out, sometimes they can see it, sometimes not. Either way it's out of their mind by the time they swipe to the next.
Sometimes I point it out, sometimes they can see it, sometimes not. Either way it's out of their mind by the time they swipe to the next.
bonifartius 𒂼𒄄
boosted
 bonifartius 𒂼𒄄
boosted

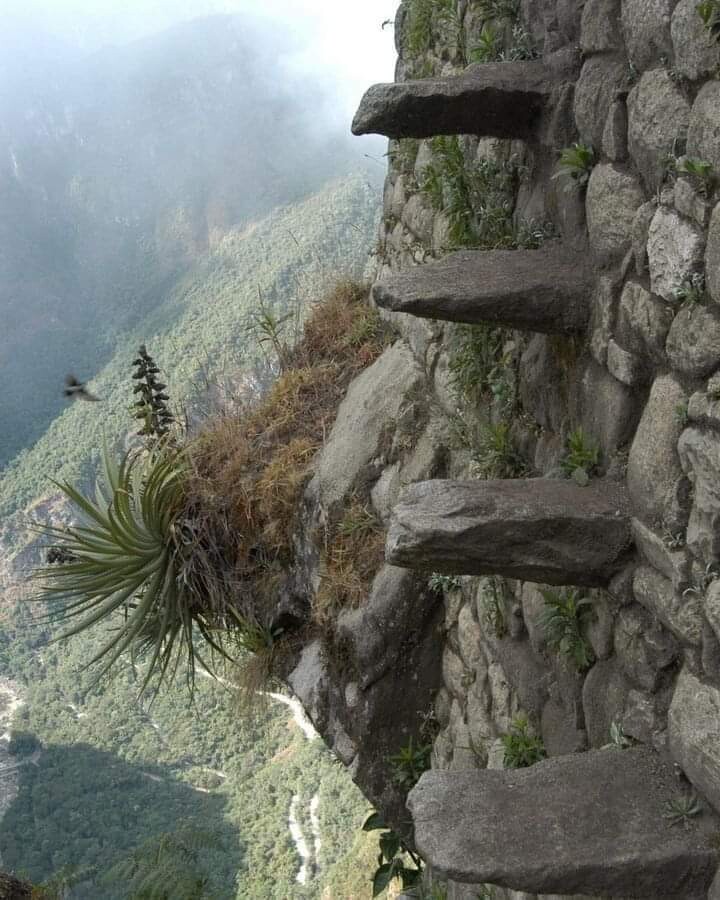
'Stairs of death' (15th Century CE), are a section of stone steps, built by Incas (1438-1533 CE), located at peak Huayna Picchu mountain, 2693m above sea level (one of steep mountains that overlooks Machu Picchu), Peru.
These stairs lead to top of Huayna Picchu, where we found Inca ruins on top.
bonifartius 𒂼𒄄
boosted

So m68k Linux people are about to break the ABI that stood for decades, because - according to them - neither the fancy new LLVM port, nor apparently Rust is flexible enough to accommodate a 32bit architecture with a non 32bit natural alignment (m68k has 16bit by default), and they assume "upstream" is not flexible enough to incorporate the changes needed, and it's "too much of a burden" to maintain.
This is exactly why we can't have nice things in software any more.

 bonifartius 𒂼𒄄
boosted

HDMI was a mistake. We should have never left God's chosen cable and connector, VGA.
ich lass das einfach mal so hier:
> In einem Interview mit der "Nordwest-Zeitung" (Samstag) hatte Kühme die AfD kritisiert. "Die AfD verdreht Wahrheiten und verbreitet Lügen", sagte Kühme. Ihr Ziel sei es, Unsicherheiten und Ängste in der Bevölkerung zu schüren. Das Sicherheitsgefühl der Menschen werde von der AfD manipuliert. Damit stelle sie sich gegen die Arbeit der Polizei.
> Kühmes Vorwürfe sind aus Sicht der GdP Niedersachsen zutreffend. Wörtlich teilte der Landesvorsitzende Kevin Komolka mit: „Johann Kühme hat in seinen Äußerungen eindeutig benannt, wie die AfD die Bürgerinnen und Bürger bewusst und gezielt täuscht, um ihre Ziele durchzusetzen. Er hat aufgezeigt, dass die Partei die Arbeit der Polizei, ihre Berichte und Statistiken missbraucht, wenn sie sie falsch darstellt, verdreht oder manipuliert."
> Komolka machte zudem deutlich, was er selbst von der AfD hält: Die Partei werde "vom Verfassungsschutz als Verdachtsfall einer extremistischen Bestrebung angesehen", zudem sei "eine ihrer zentralen Führungspersonen ein Faschist". Hinzukomme, dass "die Jugendorganisationen der AfD in mehreren Bundesländern als gesichert rechtsextremistisch gelten". Als Polizeipräsident sei es Kühmes Aufgabe, "die Bevölkerung vor dieser Gefahr zu warnen und die Polizei vor dem Missbrauch durch diese Partei zu schützen".
 bonifartius 𒂼𒄄
boosted
Here is a hopefully-useful notice about Linux kernel security issues, as it seems like this knowledge isn't distributed very widely based on the number of emails I get on a weekly basis:
- The kernel security team does not have any "early notice"
announcement list for security fixes for anyone, as that would only
make things more insecure for everyone.
- The kernel community does not assign CVEs, nor do we deal with them
at all. This is documented in the kernel's security policy, yet we
still have a number of people asking for CVE numbers even after
reading that policy. See my longer "CVEs are dead..." talk for full
details about how the CVE process is broken for projects like Linux:
https://kernel-recipes.org/en/2019/talks/cves-are-dead-long-live-the-cve/
- You HAVE to take all of the stable/LTS releases in order to have a
secure and stable system. If you attempt to cherry-pick random
patches you will NOT fix all of the known, and unknown, problems,
but rather you will end up with a potentially more insecure system,
and one that contains known bugs. Reliance on an "enterprise"
distribution to provide this for your systems is up to you, discuss
it with them as to how they achieve this result as this is what you
are paying for. If you aren't paying for it, just use Debian, they
know what they are doing and track the stable kernels and have a
larger installed base than any other Linux distro. For embedded,
use Yocto, they track the stable releases, or keep your own
buildroot-based system up to date with the new releases.
- Test all stable/LTS releases on your workload and hardware before
putting the kernel into "production" as everyone runs a different %
of the kernel source code from everyone else (servers run about
1.5mil lines of code, embedded runs about 3.5mil lines of code, your
mileage will vary). If you can't test releases before moving them
into production, you might want to solve that problem first.
- A fix for a known bug is better than the potential of a fix causing a
future problem as future problems, when found, will be fixed then.
I think I need to give another talk about this issue to go into the above in more detail. So much for me giving a technical talk at Kernel Recipes this year...
bonifartius 𒂼𒄄
boosted
Low-tech Magazine lauches a thematic book collection starting by this Internet focused edition revisiting their archive.
'How to Build a low-tech Internet?' features articles by #krisdedecker, #marieotsuka, @rra
Happy to have designed the covers for this collection. More coming soon!
https://solar.lowtechmagazine.com/2023/08/thematic-books-series/
 bonifartius 𒂼𒄄
boosted

my body is a machine that turns blue wikipedia links into purple wikipedia links
bonifartius 𒂼𒄄
boosted

 bonifartius 𒂼𒄄
boosted

Is there software around which can be hosted in a webserver which allows people to answer questions anonymously? Ideally the answers are then in some database / matrix form so one can analyze them.
#questionaires
#fedihelp
#it




- woke?
- bespoke!
- problems?
- yes, many.
- ,.-~-.,.-~-.,.-~ <°((((((((((>< ,.-~-.,.-~-.,.-~
- ,.-~-.,.-~-.,.-~ <°((((((((((>< ,.-~-.,.-~-.,.-~
- pronouns?
- sure, nouns are nice
state licensed lolbert and hypernatalist with a breeding kink. never watched rick & morty and i'm proud of it.
don't only rely on my words, read what happy customers wrote about me: "10/10 would buy again", "top seller, great value", "wildly incorrect", "teil des problems", "without imagination", "Repeated provocation using copy/paste.", "if you take a dump in my mentions, I just might notice the smell", "log out and never login again", "Du redest wirr.", "My brother in Christ, this is such a ridiculously dumb statement that I will no longer entertain this silly conversation.", "Auf Derailing-Diskussionen habe ich keine Lust. Finger über dem Blocken-Knopf.", "Wie gesagt, du kannst der Diskussion inhaltlich nicht folgen."
➡️ NO PRESSURE ⬅️ 💄NO DIAMOND💍
one day at a time.
Joined Jun 2020
